0
26
humanreader

@infosec.pub

humanreader 118 points 3 years ago

AMAs stopped being interesting a while ago. It was more like a quick press release session with celebrities trying to promote their latest stuff.

I kinda miss the IAmA part of it. People like us in usual or unusual circumstances sharing their daily lives. Researchers in remote islands, members of ethnicities or cultures that rarely get media attention, cool or unconventional jobs and how they got there. People and their stories.

path: 0 834239, hotness: undefined, score: 118, children: 6
humanreader 47 points 3 years ago

FYI, two letter TLDs are country/region/jurisdiction specific. There's an ISO standard for that.

  • .tv Tuvalu
  • .me Montenegro
  • .fm (Federation of) Micronesia

Some countries append additional modifiers to classify their uses:

  • .uk United Kingdom
  • .co.uk Company
  • ...

Three or more are generic (traditional or new)

  • .com, .net, .org, ...

In some cases, Uncle Sam said "first!" and it stuck.

  • .edu Education (MURICA)
  • .mil Military (MURRICA)
  • .gov Government (MURRRICA)

Just like what happens with Mali, what some silicon valley hipsters decide as a 'fun' acronym is just that, a fun thought. If the corresponding government decides to take away a specific domain, they probably can.

path: 0 1547888 1549794, hotness: undefined, score: 47, children: 17
humanreader 24 points 3 years ago

Speaking of which, stuff that frequently comes up in privacy related forums:

Differentiate between your professional accounts (it has your real name attached) and your non-professional ones (you use it to discuss pooping methods for example). Don't mix them up. I know many will say "so what if people in the fediverse know where I live and how I poop, I got nothing to hide" a lot, but that's how people got doxxed or swatted.

Even if you don't feel the need to, it's good to sit down and identify the potential threats given certain problems. Do you recycle passwords for email and social media accounts? What about banking? If a malicious coworker or an immature family member got access to your social media profile and posted reputation-damaging content, how bad can things get? Identify the outcomes you can mitigate or must prevent, and plan accordingly.

There is no "100%" when it comes to privacy. It's a process, not an "all-or-nothing" switch. Beginners often ask if "program X and Y will protect me 100%", and the answer usually boils down to "there isn't a single magic pill".

Privacy ≠ Security ≠ Anonymity. A VPN subscription can secure your connection (content secret in transit), but does not make you anonymous (sender known to middle node). You could leave an anonymous message (sender unknown) on a public forum, but the message itself isn't private (content not secret). And so on.

Encryption is a useful tool, but don't fall for the "military grade encryption" speech. They often mean "we just slapped whatever shit it came up with", nothing extraordinary.

There are many more but I will stop for now. No, I am not in Guantanamo.
path: 0 843137, hotness: undefined, score: 24, children: 1
humanreader 20 points 3 years ago

Google Domains, creating new ways to exploit users right before being sold off to Squarespace.

path: 0 1061543 1061586 1061587 1066076, hotness: undefined, score: 20, children: 0
humanreader 15 points 3 years ago

I've seen similar stuff multiple times, often with misquoted statistics. What many miss is that context is as important as stats.

path: 0 829857 842394, hotness: undefined, score: 15, children: 0
humanreader 14 points 3 years ago

Federation-wise it would be better if new users spread out. Between clueless redditors and impossible ideal, I prefer if they at least made an account and check out what Lemmy has to offer. The curious ones will eventually settle down and even redistribute into smaller instances.

path: 0 831826 833942, hotness: undefined, score: 14, children: 3
humanreader 12 points 3 years ago

Jesus fuck the thumbnail

path: 0 1066254, hotness: undefined, score: 12, children: 0
humanreader 8 points 3 years ago

Vietnam flashbacks of shock sites.

path: 0 1060334 1062139, hotness: undefined, score: 8, children: 1
humanreader 6 points 3 years ago

You underestimate how different some people's situations and priorities can be. For us, it's forking 10-20 USD (not a big sum of money) once a year by credit card (which isn't hard to obtain).

There are parts of the world with dire financial situations or simply outdated systrms that don't offer easy access to electric or international payments. There will be devs wanting to experiment with web services, but for them it isn't simply "forking over the bare minimum".

I won't reveal my location just for the sake of an internet discussion, but I lived in a country (It's not exactly a "3rd world shithole", but not a developed one either) where until around five to ten years ago or so getting a bank account with 'credit card' meant you 'made it'.

Why? If you weren't lucky and wanted to pay for something international, you needed a friend with the aforementioned credit card to do the transaction on our behalf. Buying on Amazon? Better make it worth before bothering our friend there. What if I wanted games on steam? The friend with credit card, or use an intermediary that charges an extra before they 'gift' the purchased game. And so on.

Now it has gotten much better, as fintech apps filled the gap offering virtual visa or mastercard payments, and the banks themselves started offering credit cards with lower quotas, but you have to remember that it wasn't available until a couple of years ago, or even still out of reach for some.

So what if you're a developer with no affordable access to international tx and want to experiment regardless? You find the ones that don't require payment.

path: 0 1555630 1555662 1556162 1556811 1558130 1564902, hotness: undefined, score: 6, children: 0
humanreader 6 points 3 years ago

Resetting federation to threads.net is even stronger proof that this was done by a 'holds sporks so randum' type of script kiddies.

path: 0 1061487 1063774 1065657 1066133, hotness: undefined, score: 6, children: 0
humanreader 5 points 3 years ago

That PRC echo chamber of a sub?

path: 0 826324 827663 827783 834341, hotness: undefined, score: 5, children: 0
humanreader 5 points 3 years ago

Free market at work!

path: 0 1550385 1551649, hotness: undefined, score: 5, children: 0
humanreader 3 points 3 years ago

I thought I had forgotten about it all. Now they're all back. I can even hear the piano from 2g1c slowly playing out. Help.

path: 0 1061487 1061546 1066168, hotness: undefined, score: 3, children: 0
humanreader 3 points 3 years ago

Certain movements making you invincible for a moment, like sitting/standing up animations from old 3d games. I don't say this because I tripped after sitting on a bench for too long.

path: 0 794196, hotness: undefined, score: 3, children: 0
humanreader 3 points 3 years ago

MBA courses must include an obligatory session of secondlife's peniscopter so no one ever bothers coming up with another iteration of this clusterfuck ever again

path: 0 1003075 1003921 1032763 1042057, hotness: undefined, score: 3, children: 0
humanreader 3 points 3 years ago

Nothing wrong with that as long as it works for you.

path: 0 997183 997331, hotness: undefined, score: 3, children: 0
humanreader 2 points 3 years ago

aalewis really secured his place did he

path: 0 1170150 1193188, hotness: undefined, score: 2, children: 0
humanreader 2 points 3 years ago

wher is my weenie i cant pee

path: 0 1035641 1041974, hotness: undefined, score: 2, children: 0
humanreader 2 points 3 years ago

Hi Mike, I recently started working as programming intern for a company doing webapps. I've worked part-time gigs in a completely different field before, that means I got no certs, no job experience in IT to speak of, I'm not the young guy fresh out of school anymore. However, my interests have always been to break into cybersecurity and have slowly added some relevant knowledge as bare minimum... linux bash scripting, selfhosting, networking and etc. I've been checking out the certs usually recommended plus all the specializations out there and gotta say this is no easy commitment, but I do want to learn.

The thing is, what I'm currently seeing as intern is very different from what people in this field usually speak of online: For example, I was expecting the latest tools and whistles, but the company I'm at uses very old (10 years) frameworks for maintenance and support for corporate clients, windows only, proprietary stuff with very little documentation online. It gets... demotivating? It's still a job and I have bills to pay, but I'm wondering how many years of experience do I need as a regular web developer (if my contract is renewed, even) to even attempt branching into infosec?

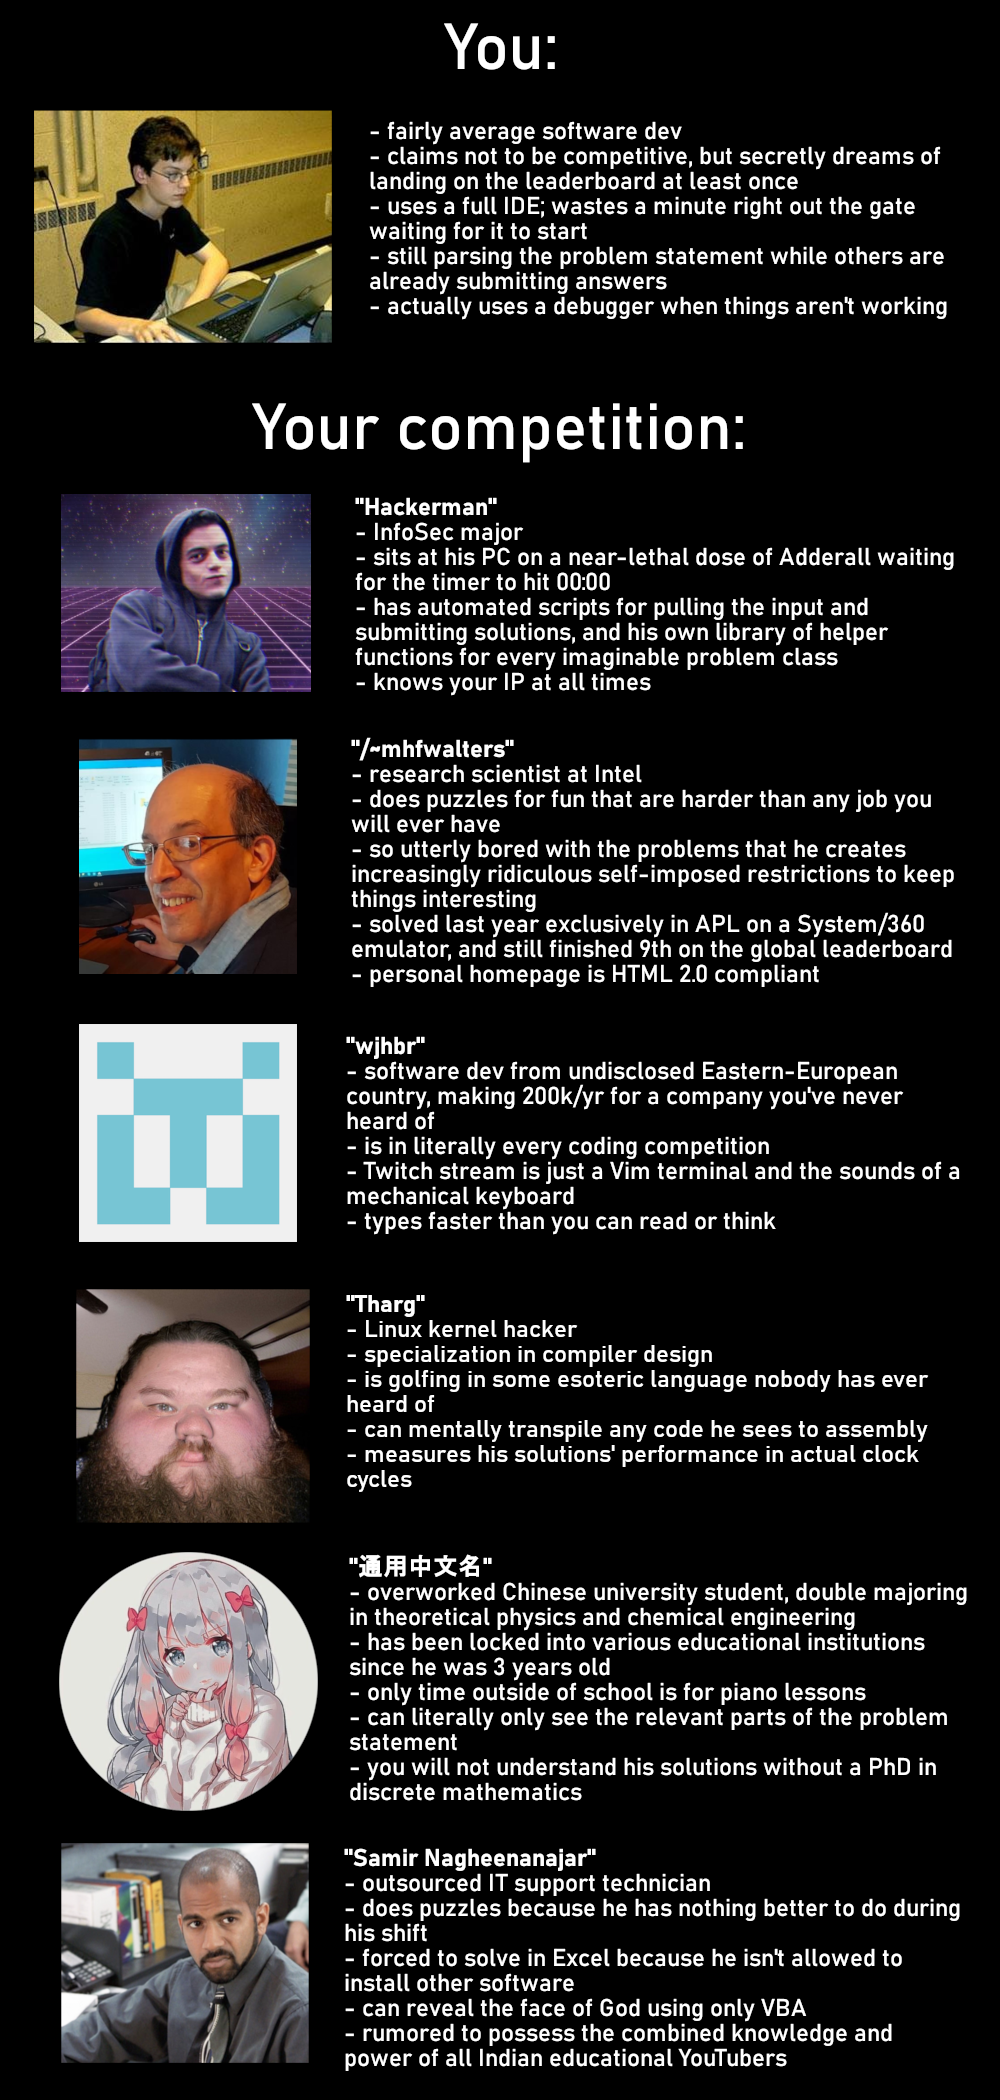
I know this gets asked a lot. Sorry for the long text. TL;DR: just started as intern programmer, company works with ancient dinosaurs instead of latest stuff, years of experience needed to become hackerman (or jumping from first one to others shown here)?

path: 0 1202203, hotness: undefined, score: 2, children: 4
humanreader 2 points 3 years ago

I see. I will have to document my progress and remind myself the company isn't actually financing this. I should start by creating a blog.

Haven't personally talked to the IT dep yet - I am in a small dev team for internal webapps and the last time we contacted them was because of printer problems, hah. Will try contacting them once I feel ready.

Thank you for the insights. Sorry I took too long to respond.

path: 0 1202203 1211033 1515126, hotness: undefined, score: 2, children: 0

thanks for using Leebra!

go to feed...