
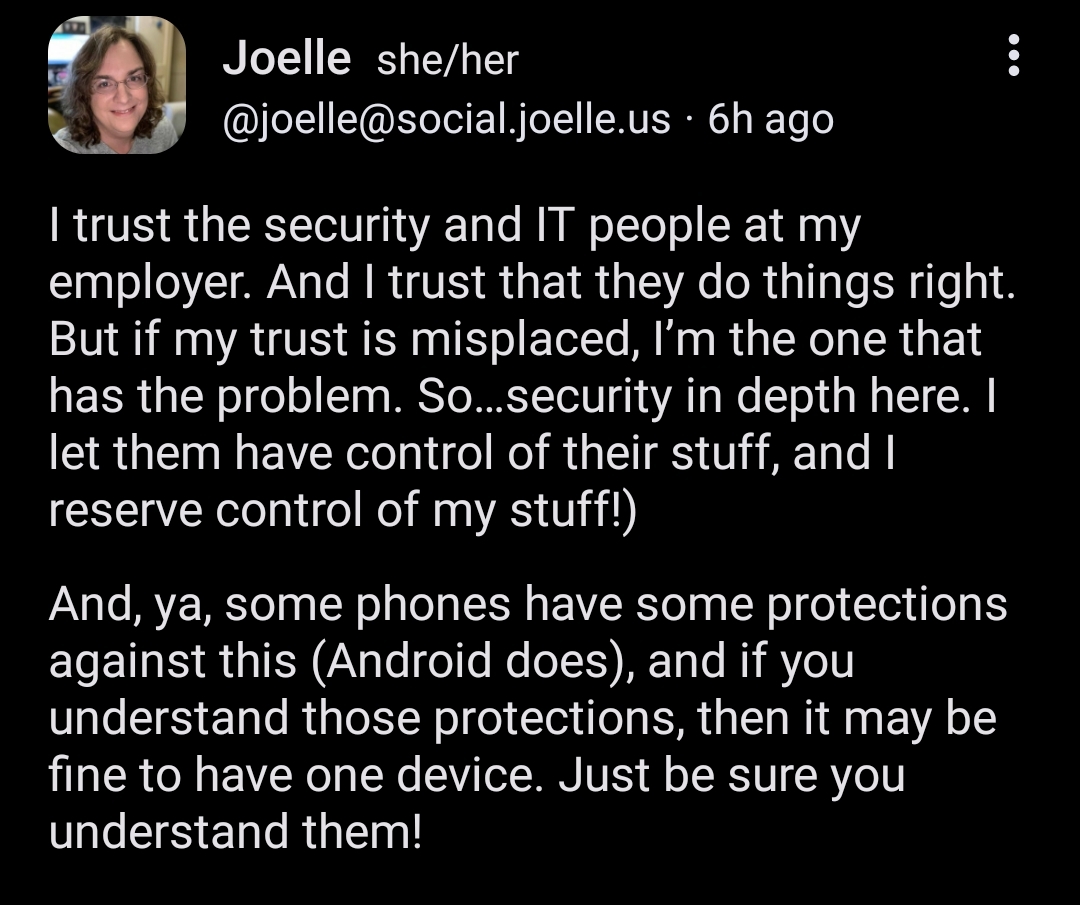
Would you give your phone’s password to your boss?
3 years ago by King to c/whitepeopletwitter
CommunicationOk3492 82 points 3 years ago
Exactly this. Any employer trying to put private devices into their MDM is totally unprofessional anyway… Most MDMs allow access to the GPS Data and have a remote wiping function, it would be a privacy mess for the employee AND employer.
tabris 61 points 3 years ago
Years ago, I worked in the IT department at a university that brought in an MDM for accessing work email on personal devices with a policy of wiping the phone if you got your unlock code wrong 3 times. I refused to use it on my personal device and told the head of the department that it was far too risky as you could accidentally do this with the phone in your pocket. He disagreed, but less than a week later, this exact thing happened to him, got his unlock wrong 3 times, phone wiped, no backup done. He still refused to change the policy even with the inconvenience it caused him. I just laughed.
ApathyTree 16 points 3 years ago
One of my colleges had MDM enabled for staff and students alike. (I realize this is likely a configuration problem, rather than malice or whatever)
The number of students who, nonetheless, did it… mind boggling.
Remote wipe? Lawl fuck no. Not worth the risk that some asshole has a bad day and wipes them all for fun.
I can understand it for certain things but.. frankly there should be some sort of like.. laws? About what your employer can require of you. Sure, company phone go for it, idgaf. But if they would need to remote wipe a device, maaaaaaaybe they shouldn’t be allowed to let employees use their own. You want full control, company, you get to pay for that with another phone, phone line, etc. (extra bonus, most people won’t carry the work phone when they are off work, so they are less reachable for unpaid labor :) )
rekabis 1 point 3 years ago
Virtually all current flip phones run either Android or KaiOS under the hood. The giveaway would be any Google app pre-installed, or any app you already recognize.
The era of “dumb” flip phones is long over. I would be very surprised if any are still being manufactured.
ares35 0 points 3 years ago
my current one actually does have an older, and very stripped-down, android.. but no google anything installed, and no google play. i don't even have a data plan attached to it--although it does have a mobile browser and can function as a hotspot.
helenslunch 1 point 3 years ago path: 0 6914494 6915322 6916465 6932753, hotness: undefined, score: 1, children: 0
jballs 16 points 3 years ago
I used to have Teams and Outlook on my phone, so I was accessible for work at almost any time. I know a lot of people think that's dumb, but I was an hourly employee so I never minded the occasional work ping after hours, since I didn't mind getting paid to reply with a few sentences from my couch. It worked out well for both me and my company.
Then they decided to make MDM mandatory on your phone to access Teams and Outlook. I declined the install and removed both apps from my phone. Now I can easily miss IMs for weeks at a time if I don't open a 2nd laptop to check them. I'm more disconnected than I've ever been, which is probably better for my mental health. I don't bill as much as I used to, but that's fine for me.
Serinus 5 points 3 years ago
I eventually caved and installed stuff on a Pixel 1.
If they wanted a phone with security updates they would have given me one.
The solution for their use should have been standard TOTP and/or yubikey. But apparently some vendor came in with a fancy PowerPoint for their proprietary project.
andthenthreemore 8 points 3 years ago
Yeah that's illegal in the civilised world.
NoIWontPickaName 11 points 3 years ago
Mine just gave us all phones.
Too much litigation chance
JoMiran 133 points 3 years ago
We have never, and will never, integrate someone's personal phone into our infrastructure. Everyone gets a company phone. If you want to use the company phone as your personal phone, or the phone you use to cheat on your husband, that's your call. Just don't complain to me when video of you pleasuring yourself end up backed up to our cloud storage and discovered by IT when tracking down large files eating up storage. (Yes that happened.)
SpaceCowboy 25 points 3 years ago
Yeah the whole thing is kinda dumb on both ends. From the employees perspective it's ridiculous to allow the company have any level of control over a device they own. From the company's perspective, why would you want to allow access and/or have information that's the company's property on a device the company doesn't own?
If I have a password for key company infrastructure stored on my personal phone, then the company fires me... well that seems like a problem a company would want to avoid. It could happen in any scenario, but significantly less likely if I have to turn in my company phone when my employment ends.
But hey the company saves a few bucks on buying phones and that helps the quarterly profits I guess.
cm0002 12 points 3 years ago
That's the whole point of work profiles and company owned devices. This Joelle just has no idea what she's talking about.
You literally can't "just install an MDM" to your phone in the way that allows a company complete access to your device. Both iOS and Android require that either the device is new or the device is factory reset. Then and only then can the device have MDM enabled as a "Company Owned Device" e.g. complete access.
The other way, is through "Work Profiles", it's an isolated and sandboxed partition. The "Work side" has no access to anything on the personal side and the personal side has no access to anything on the work side. On Android the work side has its own Play Store, its own Chrome, its own apps. (In fact, if you're rooted you can hijack the work profiles feature for yourself if you want to install apps you'd rather keep isolated, like TikTok).
If I issue a wipe command to a phone with a work profile, only the work profile gets wiped and the personal side is untouched. An employer utilizing work profiles only has visibility and control within the work profile, the rest of the phone might as well not exist
Hell, Android even gives you the ability to restrict the Work Profiles to work hours so all the work apps go dormant after 5
Dreadnaught 4 points 3 years ago
So with MDM, the company can essentially wipe that device remotely in the case that something like that occurs. Not that it's the best option. Still think companies should just provide the hardware. But that's the protection in that case.
UNWILLING_PARTICIPANT 5 points 3 years ago
Wtf how? Was someone cybering over vid chat and checked the record option?
JoMiran 21 points 3 years ago
She was recording herself, sending the video file, then deleting the file from the phone. Our phones are configured to immediately back up, so (I am assuming) that while she put together the e-mail or text, our phone was dutifully doing its job.
UNWILLING_PARTICIPANT 2 points 3 years ago
Oh man how embarassing. I imagine you make it pretty clear that the company phone comes with this capability after that incident lol
JoMiran 1 point 3 years ago
You have to sign a document before you get equipment. Part of that document is you acknowledging that you read another document that outlines what you can and cannot do with company equipment and what the capabilities of said equipment are. We even tell people to close the physical camera shutter on the laptop whenever they aren't on a video call if they want to ensure privacy. There is also a code of conduct document they need to read and sign. Using company property for lewd acts and to conceal adultery broke a number of agreements.
Taalen 86 points 3 years ago
My previous employer was acquired and the new owner required jumping through these kinds of hoops to use company email or Teams on our phones.
As an end result, everybody stopped using those on their phones. Once the laptop lid was shut, work wouldn't be bothering you until you open it the next day. Sometimes stupid things can lead to good outcomes.
half_fiction 17 points 3 years ago
Yup, to get email on your phone my employer makes you download something or other that in the fine print says they reserve the right to wipe your phone, if necessary. I saw that and now I don't have email on my phone. It's great.
keyez 2 points 3 years ago
May want to double check with your IT department. There's another comment in this thread going into more detail but your IT department could have it setup to install to and only wipe a sandboxed partition of your phone in a work profile not the entire device. I think my company docs or the app say full remote wipe but people confirmed it's just the sandboxed portion. That being said I personally didn't install the apps on my device.
UNWILLING_PARTICIPANT 13 points 3 years ago
Yeah this exact scenario happened where I used to work. The only time it's an inconvenience is if we're all in person for a tech summit or something, but having the personal contacts of a few co-workers let's me check in on any plans I might have missed.
Nowadays my phone is too old to even run slack, so I'd require work to buy me a new, separate work phone anyway.
But truth be told, it's amazing being unreachable. I logged on to the work slack today Monday morning, and found out that the company had an all hands on deck show stopper bug last Friday ~1730 lol not for me it wasn't. I was walking my dog enjoying the brisk winter air, completely oblivious until I logged back on this morning to read the postmortem. 😌
RagingRobot 3 points 3 years ago
My company gives you the option to do either. I don't want to carry two phones like a drug dealer though. Id take a beeper if that was an option lol.
Railing5132 1 point 3 years ago
Hey, let's make more e-waste!
Really, Work Profiles and a stipend are the way to go. I don't give a damn what you have on your phone - couldn't access it if I did, which I don't. If you opt to get your work email, cool - I'd like you to use the work profile, we can and would like to help you set it up. We'd really like you to have our emergency notification app due to our industry. It'll help in an active shooter situation. But you don't have to.
Steveanonymous 10 points 3 years ago
Can you elaborate? I have simple mdm on my work phone and would like to know exactly what they see and can do
Not that I am hiding anything. It’s more curiosity at this point
Posted from my personal phone
Osa-Eris-Xero512 10 points 3 years ago
This depends on the configuration of the MDM and the MDM vendor. For example, most MDM deployments to Android for instance conform to Android For Work, which functions in practice to a virtual machine from a user's perspective, and doesn't have access to a non workspace content. iOS has a similar functionality which, while less commonly used, is there specifically for use on personal devices to sandbox off 'work' content where pervasive features like factory resets and access to phone logs and sms records don't function, and you can't access the more advanced features without having purchased the device via a corporate account.
SimpleMDM has a credit card-less trial which you could set up to see what features exist and how they work from the vendor side. You won't have access to some of the 'supervised' features without being a business,but you can see the buttons offered when you aren't a corporate-purchased device readily enough.
For corporate owned devices, the rules are very different though.
ElusiveClarity 10 points 3 years ago
I have a little experience with Microsoft’s intune and there are different ways to register devices. Someone feel free to correct me because I don’t feel like logging in to double check. Company owned devices have more control and can restrict apps, lock, full wipe, etc. Personal or “bring your own” devices are much less restricted. I can’t lock, wipe, or restrict apps. For the personal devices, it’s more about giving secure access to the companies resources and not really controlling the device. I work for a small business and only use this to setup access to non important documents for employees in the field so I know just enough to be dangerous.
eddietrax 3 points 3 years ago
I can’t read your emails, text messages, I can’t remote into your phone without your permission. The info we have is very limited. You know how we can see that information? If you gave us your phone and password :-)
LilB0kChoy 5 points 3 years ago path: 0 6914537 6914893 6915244 6918401 6920633, hotness: undefined, score: 5, children: 0
eddietrax 4 points 3 years ago
Because if you are accessing company data, the company needs to ensure it’s safe. If you don’t want outlook or Teams access, you don’t have to enroll your device. In some cases companies will purchase a corporate owned device for you. An MDM allows companies to restrict copying data from work to personal and vice versa. If your device gets stolen and is compromised, it allows the company to wipe it. It can also locate the decide if it’s lost.
Grandwolf319 2 points 3 years ago
That’s something that I never understood, is the claim that default OS is just not secure… well then put all your dev hours into fixing that…
520 3 points 3 years ago
... actually they aren't wrong. MDMs are given special permissions including but not limited to reading your SMSes and phone records, restricting and monitoring your installed apps and even wiping your device.
eddietrax 45 points 3 years ago
I’m not sure what MDM you’re subjected to but I’ve been an MDM engineer for 7 years using Intune and JAMF and no, no SMS or phone records. Even the phone # is blanked out minus the last 4 digits. Yes we can wipe the devices if it’s lost\compromised but personal versus corporate owned devices are limited. I can’t see what apps you have that were personally installed. And the only info I can get are the device stats (SN, IMEI, storage, battery, memory, etc).
520 22 points 3 years ago
Intune and JAMF are not the only MDMs on the market. There are others that do offer these capabilities, at least on Android.
SMS reading:
https://support.sophos.com/...
Call log reading:
https://knowledgebase.42gears.com/...
And app lists:
eddietrax 9 points 3 years ago
Yeah I have looked at those solutions and one not on your list (MobileIron, not sure if they’re still around). I don’t know why anyone would choose those solutions but good call.
LilB0kChoy 36 points 3 years ago path: 0 6914537 6914943 6915233, hotness: undefined, score: 36, children: 6
520 5 points 3 years ago
SMS reading:
https://support.sophos.com/...
Call log reading:
https://knowledgebase.42gears.com/...
app lists:
LilB0kChoy 4 points 3 years ago path: 0 6914537 6914943 6915233 6916558 6920527, hotness: undefined, score: 4, children: 4
n1ckn4m3 19 points 3 years ago
Please cite any one of your sources. I've managed MDM for over a decade and you're spreading misinformation.
Absolutely none of the MDM products on the market allow for the reading of personal e-mail, SMS, phone records, etc. On the contrary, almost every single one provides an information screen during the enrollment that makes it abundantly clear that they do not (and can not) access that data. Moreover, the "wipe" of data is the removal of company data. It doesn't wipe your phone, it just removes the work profile (Android) or deprovisions the work profile and associated apps (Apple). All of your non-work-related data is untouched.
Quick Sources for Intune and JAMF -- do your own googling for others:
https://learn.microsoft.com/...
https://www.jamf.com/...
520 15 points 3 years ago
Absolutely none of the MDM products on the market allow for the reading of personal e-mail, SMS, phone records, etc.
So you're not aware of Sophos's MDM offering? That explicitly states they can make copies of all SMS messages?
https://support.sophos.com/...
How about call logs, with SureMDM?
https://knowledgebase.42gears.com/...
Also I said nothing about personal emails.
Moreover, the "wipe" of data is the removal of company data. It doesn't wipe your phone, it just removes the work profile (Android) or deprovisions the work profile and associated apps (Apple). All of your non-work-related data is untouched.
No, the 'wipe' can be a full factory reset.
https://learn.microsoft.com/...
Edit: typo
GroundedGator 58 points 3 years ago
While it has not yet been enforced, my employer has an MDM. Because I do not want to violate this policy or install something that gives my employer access to my device, I do not use my personal device for work and I do not have a work device other than my laptop.
This has given me some interesting perspectives.
- I do not need to be connected at all times.
- I can walk away.
- They pay me for work hours, not for my free time.
- I can easily disconnect every night and weekend, even emergencies in my area can wait.
Seems people think things are much more urgent than they should be or actually are.
ApathyTree 10 points 3 years ago
I wish I could get my partner to see it this way.. they work in IT and manage the MDM tho, and the other person with access has been partner’s friend and colleague for over 10 years, so partner is confident it’ll all be fine.
Such a dumb mindset for someone who constantly complains of being burnt out.. like no shit you are burned out, you check work emails all day/night, and handle them regardless of time..
Ross_audio 2 points 3 years ago
Blaming the MDM for this is a bit off the mark. You literally get a "Digital Wellbeing" setting you can use to set hours for your work profile on Android.
I'm not saying that concerns about installing an MDM aren't good to have or consider, just that it makes no difference to your personal choice of when to be accessible to work.
An MDM work profile is much easier to set that boundary with than being logged into the apps directly.
Tell your partner you want them to try the setting.
ApathyTree 2 points 3 years ago
I’m not blaming it on that, I was saying I just wish I could get my partner to have the mindset of the person I was replying to. But they won’t because they are in charge of said system so don’t see the privacy hit, and that’s all they are focused on.
They have cut down use when around me but.. meh, all I can do is encourage stepping back a bit, they have to actually do it and.. won’t.
cm0002 1 point 3 years ago
https://support.google.com/...
You may want to pause your work profile when you're not working. For example, at the end of your workday, over the weekend, or when you're on vacation.
When your work profile is paused, work apps won't run, generate notifications, or consume data and battery life. You also won't be able to access work apps or widgets. If you try, you'll see a message asking if you want to turn your work profile on again.
You can pause a work profile on Android at any time and it won't let you open them until the user decides to run them again
Your partner doesn't disable the work profile because they don't want to, not because they can't (Or can't because of company policy/culture)
ApathyTree 2 points 3 years ago
I know it’s by choice, that’s why it’s frustrating.
cm0002 76 points 3 years ago
Don't pay attention to this Joelle person, she has no idea what she's talking about (Or does and is spreading misinformation intentionally)
You literally can't "just install an MDM" to your phone in the way that allows a company complete access to your device. Both iOS and Android require that either the device is new or the device is factory reset. Then and only then can the device have MDM enabled as a "Company Owned Device" e.g. complete access.
The other way, is through "Work Profiles", it's an isolated and sandboxed partition. The "Work side" has no access to anything on the personal side and the personal side has no access to anything on the work side. On Android the work side has its own Play Store, its own Chrome, its own apps. (In fact, if you're rooted you can hijack work profiles for yourself if you want to install apps you'd rather keep isolated, like TikTok).
If I issue a wipe command to a phone with a work profile, only the work profile gets wiped and the personal side is untouched.
Hell, Android even gives you the ability to restrict the Work Profiles to work hours so all the work apps go dormant after 5
apqnxhfriqhfjxrrcxs 13 points 3 years ago
In fact, if you're rooted you can hijack work profiles for yourself if you want to install apps you'd rather keep isolated, like TikTok
You can use Shelter to enable this functionality without root.
Curlyshrew 3 points 3 years ago
Exactly.
These services are containerised on personal devices so that its services can only be administered within the app container.
It has limited to no control over the phone itself or apps outside of its MDM container in the context of personal devices.
egonallanon 3 points 3 years ago
There's also the option for MAM apps as well which I quite like as light touch management option for ios and android. Essentially limits control to select apps and even then just the company data in those apps.
Ross_audio 4 points 3 years ago
The setting is in the wrong place in my view. It's under
"Digital Wellbeing & parental controls." > Work Profile Schedule
Simple from there.
I never look in parental controls as I have zero need so I had to look it up when I was searching for it. Personally I think "Digital Wellbeing" and "Parental Controls" should be entirely separate.
I set mine to come on an hour before and after work as a buffer and love it.
cm0002 3 points 3 years ago
Here you go: https://support.google.com/...
MIDItheKID -1 points 3 years ago path: 0 6922867 6923612 6929986, hotness: undefined, score: -1, children: 0
yokonzo 4 points 3 years ago
I worked in a place that required this, it was basically a time clock app, but it detected automatically if your phone supported work mode which allowed it to be basically sandboxed in it's own virtual space., I've also run into school apps that do this
yokonzo 1 point 3 years ago
No we were contract workers, we traveled to different job sites so our clock in also had to be mobile. I mean you COULD do a clock in sheet if you downloaded it from the depths of their website and then filled it out and mailed it in weekly by snail mail buuuut
sugar_in_your_tea 3 points 3 years ago
We're required to use a MFA app, but it has minimal access to the system. It literally just prompts for an "Is this you?" with a fallback to codes if the network connection goes down.
I also have Teams and Slack installed for team communication, but that's optional and also has minimal access. Teams has an login helper thing installed as well, and I'm not really sure what it does, but it didn't require any special permissions.
I suppose I could refuse, but that would just be a pain for everyone since I'd either need to use someone else's device or they'd need to get one just for me. Seems kinda silly imo.
My last company wanted my phone to be connected to the Google Apps thing, but it allowed my boss to remote wipe, so I refused. It wasn't required, and most people said no, but it was a thing they recommended fairly strongly.
Snapz 1 point 3 years ago
So curious, did your job listing mention you needed to own a smartphone as a requirement? Feels like they are probably riding a line where this is made to "feel" required, but legally they are careful of their wording or they may have some issues with your local labor board.
sugar_in_your_tea 1 point 3 years ago
No, but I'm in a technical role where pretty much everyone has one anyway. Our company culture is such that they'd find a workaround (e.g. provide a phone if needed).
My last role required a smartphone, and we got ~$50/month on our paycheck to pay for it. My current job doesn't "require" anything, it's just strongly recommended.
Snapz 1 point 3 years ago
I think in that scenario,, you could separately open an account with a cheap provider that includes a free, cheap phone and dedicate its use to only work. So yes, pain in the ass worth extra steps, but not a requirement to use your own phone.
I think it's garage regardless, if they need you to have a phone, they should fully provide, but just pointing out that it's legal fuckery on their part as it's meant to confuse/scare people into thinking they don't have a choice.
mp3 33 points 3 years ago
It depends how the MDM is implemented. If it allows locking and wiping the entire device, no. If it makes a sandbox for the work stuff, and it only grant them access to control, lock and wipe that sandbox then I don't mind.
That's what we do for personal devices, corporate devices are fully managed/supervised.
0110010001100010 18 points 3 years ago
Yeah my work MDM is setup this way with Android Enterprise. Everything work-related is isolated to that area and there is no other access to the full device. I can even have all those apps shut off after-hours or when on vacation so I don't get notifications during personal time. My boss knows to text/call me if there is something urgent that comes up.
ParetoOptimalDev 14 points 3 years ago
Software is imperfect and you shouldn't trust that future updates will not add that ability.
Gestrid 5 points 3 years ago
Typically, the app needs to ask for permissions like that, though. On Android, they need to ask to become a "Device admin", and they need to specify what specifically they'll use that access for. I imagine (though I'm unsure since it's never happened to me) they need to ask to update those permissions if they want their uses to change.
ParetoOptimalDev 3 points 3 years ago
Agreed, but its not perfect. I recall but couldn't recover a link to a story about some application bypassing android or iPhone permissions.
Another big recent flaw allowed apps without the permission to draw over other apps.
prettybunnys 27 points 3 years ago
You want me to check email outside of work hours …. Better provide me a phone and money for that.
ExpensiveConstant 17 points 3 years ago
SUPER depends on the platform. If you own an iOS device and enroll it in MDM through the settings app, MDM ONLY has access to whatever it puts on the device
Aceticon 15 points 3 years ago
If you have work stuff on your personal device, any legal proceedings against the company might mean your personal device is taken as evidence, all of the data in it will get examined and you might only get it back years later.
So even if only for legal reasons, never have company stuff in a personal device, quite independently of there being some fancy tech or other to virtually partition it.
cardboardchris 15 points 3 years ago
Setting aside the issue of whether this post is overstating the risk of MDM software on a personal phone, I had a tangentially related experience that might provide a tip for anyone who's in a similar situation.
I like to have the convenience of checking my work messages and chats on my personal phone, so I have Teams and Outlook installed and using my work account.
When I first went to sign in to my work account on Outlook, I got this message like "Outlook needs to run with administrator privileges in order to provide the necessary security for this account" and shunted me off to some system settings to approve the permissions. Big nope.
So I tried Outlook Lite, and it made no such demands and works perfectly. So for anyone else who's run into this, try Outlook Lite! I hope this helps somebody.
brakenium 3 points 3 years ago
Sadly you won't always have a choice. My university has disabled any non-Microsoft client support. They do this to "protect the privacy of the teachers". Currently I'm running a windows VM on my server with Outlook to forward the emails to my personal email. Which in the end is even worse for them GDPR wise
crackajack 1 point 3 years ago
I didn't even know there is lite version.
wheeldawg 13 points 3 years ago
I wouldn't do this. Sandbox sounds good, but that kind of access is just to shady to want anywhere near my device.
I've never had to download an app for work. But I wouldn't deal with an MDM at all without a gun pointed at me.
DoctorWhookah 28 points 3 years ago
MDM admin here. I’m much more familiar with iOS, but newer versions of Android will completely sandbox work profiles from the personal side. Work stuff will be encrypted and the admins cannot access anything outside of that.
assaultpotato 15 points 3 years ago
Yep. Work profile and apps are completely disparate, and it's actually kind of tough to transfer any data across the boundary even if you wanted to. Any time I need to send a picture to my work Slack I have to remind myself to use the work profile camera app.
It's the same tech that powers the Secure Folder thing in Android devices. My older S8 was on Android 8 or 9 and still had this functionality, so I'm not sure how old you'd have to go to have a less secure setup.
I think this mastodon post is inaccurate.
kryptonianCodeMonkey 5 points 3 years ago
I don't have an exhaustive understanding of how it works and limits data, but on my android, it essentially has two partitions, one for personal and one for work. They do not share data. In order to take and share a photo on my work Teams chat, it has to be taken either from within teams or with the camera app on the work partition. It cannot access my personal gallery. I have Teams on my personal partition from an old job that I still help out from time to time, and the same exact Teams app installed on my work partition. They are not connected in any way. The only thing that doesn't require me to put in a pin to access on my work parition are the notifications.
Most of the limitations I experience from my side are in my own access to work resources. I can't say with confidence that those same limitations go both ways. But it does seem like that is probably the case.
plaguesandbacon 2 points 3 years ago
Within the Intune MDM space, a separate partition is created on the device that essentially isolates work apps/data from personal apps/data. I, as a sys admin, have control over the "work" space, but no control over the personal side of things.
We don't have a very heavy handed approach to monitoring usage etc for mobile devices or even laptops and this has been the case with most of my previous jobs.
That said, I'm sure there are IT departments out there with a ton of staff and a big budget that can and will get quite granular with what you are doing on your devices (keylogging, etc)
TheWilliamist 5 points 3 years ago
I’ve been using Google’s native MDM. I can’t do any of those on a personal device. The only thing I can do with a personal phone used for work is wipe the android for a work profile off of it. If you’re using a company device, I cannot do any of that. The only thing I can do is wipe the entire phone and that’s it.
CosmicTurtle 5 points 3 years ago
100%
I used to do MDM at my last company. The post here is very misinformed on how it works.
All companies can do is wipe your phone and configure settings. They cannot read what's on the phone, except for the stuff in the work profile and even then it's limited.
I have a corporate phone with a personal and work profile set up and have no issues browsing porn. That's how confident I am.
The only risk is if you're on a regular cellular network, your company could ask the mobile network to send the sites you visit. But if you're VPNing or on your home wifi, that won't tell them much.
dejected_warp_core 3 points 3 years ago
This is the employer working around having to purchase and maintain a phone inventory for employees.
While we're on the topic, this also applies to laptop/desktop hardware for the work-from-home crowd.
In general it's a bad idea to use personal devices for work. Companies that don't give you a choice are being cheap and disrespecting of privacy at best, and want to spy into your personal life at worst. It's also really, really, really bad IT security for everyone involved.
RememberTheApollo_ 3 points 3 years ago
TL;DR - never use company devices for personal materials. Create a separate, independent email strictly for work or your company email for all company devices, not your personal one.
I have a mobile device required for work, and my personal device.
No personal stuff goes on the work device. Photos, apps, logins, messaging, whatever. Zero. However, many of my colleagues use the device like, “Free mobile device, bro!” and load it up with everything they have on their personal device.
That is a horrible idea. The company device has its own cybersecurity app installed and managed by company servers that sees everything on your device, and should your device be used for something it shouldn’t, they don’t even have to take it from you to know what you did. They know when you did it, too. Watching movies or texting while driving? Reading a book or using social media while monitoring a system? If you crash the company car, or the system goes TU and they see you were fucking around with the company device instead of doing your job, you’re fucked. They see it all, it’s all regularly scanned, uploaded, screened, whatever. They just don’t bother to look unless they need to. Already had a couple people fired for illegal material on their devices.
quicksand 1 point 3 years ago
When I set up the device management on my work phone, it explicitly said it couldn't see media files on my phone. And particularly it didn't touch the non-work profile. Do you have a source that contradicts this?
INHALE_VEGETABLES 1 point 3 years ago
I quit my job of over a decade using the same phone and email, I left to go competition. I gave them all my passwords.
I've kept my personal phone a lot longer than I had theirs lol
LemmyIsFantastic -1 points 3 years ago
Separate profile and container. Idiot meme.
derpgon -3 points 3 years ago
Easy solution, use Linux. No extra permissions, no spying, and everything worked for me so far. Android has a neat feature for a separate work account. It used to be called "work acxount", but it's not there anymore and you have to use "secure folder", or whatever it is called now.
13617 1 point 3 years ago
When you sign into your works Google account or intune usually it will set a work profile up. If you want to set one up without this, or just want your own personal space for secondary apps you can install an app called "Island" from the play store.
I wouldn't recommend shelter as it bricks the functionality of the work profile on newer versions of Android.
pearsaltchocolatebar -5 points 3 years ago
But, in all honesty, no one is going to be looking at it unless there's a very good reason too. IT sure as hell doesn't have enough resources to monitor it.
MDM largely exists to remote wipe a lost or stolen phone.
RunawayFixer 3 points 3 years ago
In reality, yes there will be snooping. I've had a new colleague that had to explain why they had parked several times near the HQ of a competitor outside working hours. Answer: he lived in that village and his favorite bakery was were he had parked. After that he removed the company tracker from his car, a car that he was leasing and paying for himself. He had only installed the tracker as a courtesy to facilitate on site personnel tracking and it was abused in the shortest order.
Anything that can be abused, will be abused.
whitepeopletwitter
@sh.itjust.works
10495
2064
4588
People tweeting stuff. We allow tweets from anyone.
RULES:
- Mark NSFW content.
- No doxxing people.
- Must be a pic of the tweet or similar. No direct links to the tweet.
- No international politcs
- Be excellent to each other.
- Provide an archived link to the tweet (or similar) being shown if it's a major celebrity, figure or any politician
- https://www.sotwe.com/
- https://twitterviewer.net/Note: Archive.is is no longer recommended because they remove/alter content.
- If a tweet (or similar) makes a statement of fact, either mark it as "satire" in the body or provide the original source link backing up the statement (see rule 6)
go to feed...
save