
We've all been there.
Wish_you_were_a_beer 32 points 3 years ago
Haha this is great, got to the chess part before giving in 
Mic_Check_One_Two 15 points 3 years ago
Same. My country was Jordan. Took way too long to figure out, because it dropped me in the middle of an empty amphitheater with no visible road signs, license plates, etc…
catastrophicblues 11 points 3 years ago
I just pasted all the countries and ditched the ones that were wrong.
edgarallenpwn 2 points 3 years ago
I'm starting to want to learn chess after learning about the password game. I need to go get further!
AlGoreRhythm 2 points 3 years ago
Qxh6
TrontheTechie 10 points 3 years ago
Bruh, it just made me google dork to find out where a random street view was. 10/10 would recommend
lackthought 8 points 3 years ago
I gave up at the 'find a youtube video of an exact length' step
my laziness limit had been reached
nieceandtows 4 points 3 years ago
It was great until that step 20 where some 'fire' deleted everything I made. It's one thing to make you think, it's a completely different thing to just delete everything and make you start over. Fuck that noise.
dandroid 3 points 3 years ago
Yeah, I just got to the password on fire and survived, but I wanted to move Paul to an edge so he doesn't get killed if there's another fire. But apparently cutting/pasting him kills him. :(
Edit: I went back and got to rule 25. Rule 24 was a bitch and a half, but I did it. Then I had to sacrifice letters, and I thought, oh, I can't use M or D because they are roman numerals for 1000 and 500, so I chose those. It included lowercase as well, and that made some previous rules impossible. In my anger, I may have overreacted, because I intentionally overfed Paul to kill him.
nieceandtows 2 points 3 years ago
That’s brutal
Rozz 2 points 3 years ago
I got stuck on rule 14 where I had to guess the country in Google maps.
Au2WonderfullyshellnIcepigsXXXV!85mayy4n6mfiend🌘
I guess it's kind of secure. Does the password change daily with the current wordle word?
ghostcookies 2 points 3 years ago
it does change a lot with every try
nowwhatnapster 16 points 3 years ago
Should be: "your password cannot be one of your last 24 passwords"
Tyler_Zoro 6 points 3 years ago
Yeah, this is important. Make it a really big number too so that I have to change my password lots of times in a row in order to put it back to what it was. ;)
VindictiveJudge 6 points 3 years ago
Especially for those places that want your password changed every two weeks.
UncleRummy 2 points 3 years ago
Or just append a letter that increments every time you change your password, and keep a note of what the current letter is.
Passworda
Passwordb
Passwordc
...
When your z password expires, just wrap back around to a.
quat 1 point 3 years ago
At my work they wanted better security, and made the rule of minimum 12 characters, must include all sorts of numbers, special characters, etc, no previously used password and it must be changed every month, 3 attempts then the account is locked and you have to call IT.
The result was that people wrote their passwords on post-its on the screen, so it led to worse security overall and they had ro relax the rules.
Buddahriffic 13 points 3 years ago
It follows the vein of some of the password rules and feedback reducing security itself. Like why disallow any characters or set a maximum password length in double digits? If you're storing a hash of the password, the hash function can handle arbitrary length strings filled with arbitrary characters. They run on files, so even null characters need to work. If you do one hash on the client's side and another one on the server, then all the extra computational power needed for a ridiculously long password will be done by the client's computer.
And I bet at least one site has used the error message "that password is already in use by " before someone else in the dev team said, "hang on, what?".
zeppo 6 points 3 years ago
It's true, most of these rules are harmful, but also most are in common use and accepted, for some reason. I have heard of a password system that had that warning, perhaps even the account, but it was in a softwaregore screenshot context.
poplargrove 8 points 3 years ago
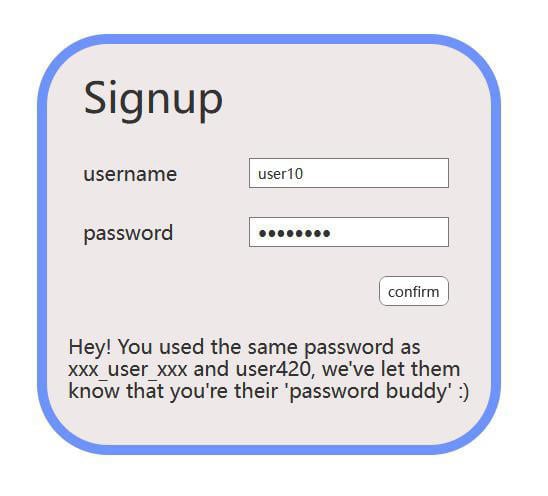
Tyler_Zoro 42 points 3 years ago
Fun fact: password controls like this have been obsolete since 2020. Standards that guide password management now focus on password length and external security features (like 2FA and robust password encryption for storage) rather than on individual characters in passwords.
fubo 23 points 3 years ago
Since 2017 at least; and IIRC years before that; that's just the earliest NIST publication on the subject I could find with a trivial Web search.
https://pages.nist.gov/800-63-3/sp800-63b.html
Verifiers SHOULD NOT impose other composition rules (e.g., requiring mixtures of different character types or prohibiting consecutively repeated characters) for memorized secrets. Verifiers SHOULD NOT require memorized secrets to be changed arbitrarily (e.g., periodically). However, verifiers SHALL force a change if there is evidence of compromise of the authenticator.
"Memorized secrets" means classic passwords, i.e. a one-factor authentication through a shared secret presumed to be known to only the right person.
Rufio 10 points 3 years ago
I wouldn’t say obsolete because that implies it’s not really used anymore. Most websites and apps still use validation not too dissimilar from the OP, even if it goes against the latest best practices.
ArianaGrande 8 points 3 years ago
Yeah, the most recent one for me was creating a password at lemmy.world
Tyler_Zoro -2 points 3 years ago
I wouldn’t say obsolete because that implies it’s not really used anymore.
I'm not sure where you heard someone use the word "obsolete" that way, but I assure you that there are thousands if not millions of examples of obsolete technologies in constant and everyday use.
Rufio 4 points 3 years ago
https://www.merriam-webster.com/...
no longer in use or no longer useful
toomanyjoints69 -1 points 3 years ago
Yeah i agree. The best example of this is Linux. To anyone who disagrees, why does a modern operating system require you to use a terminal, or edit config files instead of changing settings in a gui?
Its THE example of ancient software being pushed on to niave techies that would rather have an insecure open source project than a safe, walled garden like Microsoft Windows 11.
Although Windows 11 does have its problems. The chief of which is bogging down the streamlined simplicity with things a normal user wont need like a package manager.
Tyler_Zoro 0 points 3 years ago
The best example of this is Linux.
Ouch... so, you might want to learn more about technology before commenting in a Technology community...
why does a modern operating system require you to use a terminal
Because a terminal is one of the most powerful modes of interaction ever invented. It can serve as a relatively low-tech UI, but it is also simple enough to be used as a machine interface. It is lightweight, works even when other protocols and interfaces are thwarted by infrastructure issues, because it is simple text, but also meant to be read by a human, it can make for a great interface for logging, you don't have to guess at which obscure standard (if any) to use to talk to it, compliance with relevant standards is baked into nearly every language ever written, etc.
Try building a system like Kubernetes on graphical UIs... I dare you.
Its THE example of ancient software being pushed on to niave techies
What industry are you working in?! AWS is nearly all Linux. Google Cloud is nearly all Linux. Android is Linux. Hell, even Microsoft finally relented and is now strongly supporting their Windows Subsystem for Linux (WSL) because it's necessary for supporting modern cloud applications.
that would rather have an insecure open source project than a safe, walled garden like Microsoft Windows 11.
Okay, this has to be a troll... right? This is a troll? Please tell me you can't be serious.
CoderKat 7 points 3 years ago
For today's 10,000 who have never seen it, https://xkcd.com/936/ succinctly explains why the whole mixed character types thing isn't favoured.
EmpatheticTeddyBear 1 point 3 years ago
I'm still waiting on an XKCD that references #936 with the fact that we soon as we have reliable, functional quantum computing, all of the passwords from before that point in time will be completely and utterly broken. That the only way to make a password that a quantum computer would have a tough time breaking is if it was made by another quantum computer. Unless of course the comic has already been made and I just missed it, which is a complete possibility because this year for me has been utterly crap.
Archpawn 2 points 3 years ago
Some of them are broken by quantum computers, but not all of them. For example, SHA256. You can use Grover's algorithm to take sqrt(n) steps to check n possible passwords, which on the one hand means it can be billions of times faster, but on the other hand, you just need to double the length of the password to get the same security vs quantum computers. Also, this is the first I've heard of a hash that uses a quantum computer. Do you have a source? Hashes need to be deterministic, and quantum computers aren't, so that doesn't seem like it would work very well.
Maybe you're getting mixed up with using quantum encryption to get around quantum computers breaking common encryption algorithms?
Tyler_Zoro 2 points 3 years ago
soon as we have reliable, functional quantum computing
Which we've been told is right around the corner for decades. The issue is that QC doesn't scale up. If you try you get vastly more noise than signal. Current work in QC is all aimed at reducing that noise, but even for only 70 qbits, the current state of the art can't eliminate enough of the noise for QC to be useful in most applications.
The only places it's currently bearing any fruit is where all of the extra work to reduce noise and the delays that incurs are irrelevant because there is no classical approach at all. But even then, the costs are enormous and the benefits are miniscule.
Proweruser -1 points 3 years ago
Except you can run a dictionary attack on that and suddenly it's only 4 variables that are cracked way faster than the first password.
Proweruser -1 points 3 years ago
Except you can run a dictionary attack on that and suddenly it's only 4 variables that are cracked way faster than the first password.
cley_faye 3 points 3 years ago
People should be made aware of all the tools available to properly manage tons of passwords. Not even going too deep into "passkey" stuff or any modern shenanigans, but a password manager used to generate random passwords for each separate sites is such a simple step.
Tyler_Zoro 1 point 3 years ago
I take a tiered approach: I use Chrome's password manager for things I don't care all that much about. I use PasswordSafe in a shared file in cloud storage for passwords that I care a bit more about. And for those very few that are incredibly important to me, I just memorize the password that's usually made up of some long nonsense phrase (e.g. "apple youth brandish frobnitzer brainiac") which has enough obscure words to necessitate a very hefty dictionary to crack (or even a made up word or two).
Of course, I also have to memorize my Google and PasswordSafe passwords, since writing those down would compromise the first two storage systems.
mudmaniac 36 points 3 years ago
For those wanting to play this as a game, there is this wonderfully fiendish website.
https://neal.fun/password-game/
Rule 13 Your password must include the current phase of the moon as an emoji.
afraid_of_zombies 4 points 3 years ago
I got stuck on the chess one. Used to think I was pretty decent at the game. After a few tries I gave up and tried a few websites that claim to be able to solve it and none found the "correct" move.
eochaid 35 points 3 years ago
Sorry, that password is already in use
BIG red flag. Abort. Abort.
Also I love when they only support certain special characters. So the psuedo random noise created by my password generator won't work until I curate out the unsupported characters.
dancing_umbra 20 points 3 years ago
I was changing my password on a pretty big company website the other day.
The password generated by my password manager kept giving me a http error (500 I think)
I generated a new password and deleted all the special characters other than the obvious ones. Boom, worked first time.
So looks like someone is not sanitising their inputs properly.
I sent them an email so hopefully they will fix.
dandroid 11 points 3 years ago
I sent them an email so hopefully they will fix.
One can only hope. But based on my experience, they usually do not. I once sent an email to Microsoft telling them that their Microsoft account app had a vulnerability, and I even sent them the XML line they needed to add to their Android Manifest to fix it, and they wouldn't do it because it required physical access to the device to exploit. I mean, that's fair enough, but it was literally one line of code to plug the hole.
They eventually did add that line about 6 years later.
dancing_umbra 9 points 3 years ago
It boggles sometimes.
I remember about 2015 (?) In the vicinity anyway, PayPal has a 12 character MAXIMUM on their passwords.
PayPal, you know the place where you can literally transfer all the money. A 12 character MAXIMUM
I emailed them to suggest they change this requirement. And they replied saying that 12 characters was sufficient if you used special characters and numbers.
Glad they have finally changed it now.
Pumpkinbot 7 points 3 years ago
Password1'); DROP TABLE Passwords;--
pfannkuchen_gesicht 8 points 3 years ago
Funniest thing was when I registered on a website which parsed the \0 sequence and hence truncated the password in the background unbeknownst to me. This way you could circumvent the minimum length and creare a one character password.
magic_lobster_party 6 points 3 years ago
Once I registered on a website. I used an auto generated password. Next time I tried to log in to the website I was confused that my stored password didn’t work. Requested to change the password, but I used the stored password again. To my surprise, it said the password must be different from the current one.
After a bit back and forth I finally figured it out. Apparently the site had a max length on the password. Any password longer than that is truncated. This truncation wasn’t applied in the login form. Only when creating a password.
Trapping5341 1 point 3 years ago
I always just refresh the password until I get a random one without the characters the randomly choose to forbid 😂
SevenDigitCode 33 points 3 years ago
My favorite, though, is:
types in password "Password incorrect" goes to reset password "please enter a new password" types in password "your new password cannot be the same"
stephen01king 6 points 3 years ago
That just means you entered it wrong the first time.
5too 6 points 3 years ago
Exactly this. I want to normalize showing the password requirements when you don't immediately get the password - if you made me jump through hoops the first time, at least remind me what they were!
mycelium_underground 9 points 3 years ago
i have had this happen on some websites occasionally while using my password manager.
tony 6 points 3 years ago
Sometimes it means the page checking the password is following a different ruleset eg. the main page is case sensitive and the change password page isn't. Sometimes it's stuff like the entered password is silently truncated to a fixed number of characters and because of that won't let you log in. Sometimes it's wierd character expansions being passed directly to the password checking routine (& or similar).
average650 30 points 3 years ago
The worst part is that if they know that password is already in use.... then they aren't storing their passwords appropriately.
average650 31 points 3 years ago
yes, but then they are not salted, which is what they should be doing.
Kolrami 18 points 3 years ago
True, but for the same big O they can salt the password for each user and compare it to what they have stored. My big pet peeve (that I've actually seen) is when they say your password is too similar to an old one. I have no idea how that could be reasonably done if they're storing your password correctly.
Bluehood380 13 points 3 years ago
But are they peppered?
FluffyPotato 28 points 3 years ago
The worst one is when it only supports up to like 16 characters but doesn't tell you so it will only use the first 16 characters and ignore the rest. The next time you need to enter it and get the 64 character password from your password manager it will just say it incorrect and you're left with no idea on why it's wrong.
akash_rawal 2 points 3 years ago
This was me on a bank's site till I clued in that I need to shorten my password.
MidwestComrade 3 points 3 years ago
Sometimes there's a limit on the length but it's only imposed by the JavaScript of the website, so I can use my password manager to insert the text directly into the field but I can't actually type it in.
😐
confetti_8tVST5 2 points 3 years ago path: 0 1274932 1321661, hotness: undefined, score: 2, children: 0
001100010010 28 points 3 years ago path: 0 1263114, hotness: undefined, score: 28, children: 20
BettyWhiteInHD 23 points 3 years ago path: 0 1263114 1263593, hotness: undefined, score: 23, children: 19
voidMainVoid 14 points 3 years ago
It's a lot easier to remember that than #@?Zk23!nPw
BettyWhiteInHD 3 points 3 years ago path: 0 1263114 1263593 1264245 1265065, hotness: undefined, score: 3, children: 0
rebelsimile 2 points 3 years ago
Tacking onto this, because I mix password types too, I don’t want all my passwords in the same (even pseudorandom) style.
Affidavit 5 points 3 years ago
Spoken like someone who has never had to deal with corporate 'security' before. Password managers are great, but if your workplace has incompetent IT (e.g. probs 90% of workplaces), then you're SOL and must play the increments game.
TurboDiesel 5 points 3 years ago
Yeah, I switched from LastPass (after one of their many data breaches) to 1Password. I don't know any of my passwords anymore because they're all just generated and saved automatically. And that's a good thing.
ozymandias117 2 points 3 years ago
Tons of websites reject pseudo randomly generated passwords, too
BettyWhiteInHD 6 points 3 years ago path: 0 1263114 1263593 1266173 1266300, hotness: undefined, score: 6, children: 1
ozymandias117 2 points 3 years ago
That’s inherently blocking pseudo random password generators.
Max length doesn’t bother me if it’s at least 128 characters, but only allowing specific special characters is a sin.
As of last year, Wells Fargo’s passwords were even cause insensitive. Dunno if they’ve fixed it since then, but probably not
ultimate_question 1 point 3 years ago
Because I want control of my passwords in my head not some software, it's not like a string of random characters is any more secure than one that can actually be remembered
BettyWhiteInHD 5 points 3 years ago path: 0 1263114 1263593 1266386 1266427, hotness: undefined, score: 5, children: 1
ultimate_question 1 point 3 years ago
Yes because I have an easily remembered system for a unique passphrase for any given site. Not trying to shit on password managers though, just providing a different perspective
eth0p 8 points 3 years ago
Had to give up at rule 20 because I was using a phone.
Spoiler
As much fun pain as that was, highlighting with a touch screen is nowhere near fast enough to put out the fire.
Would love to see a speedrun leaderboard for this, though.
Demonmariner 4 points 3 years ago
Me too.
CoderKat 4 points 3 years ago
Fuck. I gave it a try for real this time and hit a permanent game over condition.
spoiler
Apparently you can overfeed Paul
Darn, I wanted to see what came next. Some of those rules were hilarious. But I'm not doing that all again.
chicagohuman 1 point 3 years ago
That was my limit too!
complacent_jerboa 2 points 3 years ago
I got to the "wordle" one before giving up. jesus lol, nice meme
afraid_of_zombies 2 points 3 years ago
It was crone btw.
complacent_jerboa 2 points 3 years ago
wow, spoilers /jk
confetti_8tVST5 25 points 3 years ago path: 0 1288035, hotness: undefined, score: 25, children: 12
setsneedtofeed 12 points 3 years ago
Unfortunately a lot of jobs require passwords and they use outdated security processes, forcing people to have the old fashioned “must have uppercase, lowercase, number, and special character & you have to change it every 3 months for no reason” passwords instead of the stronger (and less annoying) alternatives.
funkless 10 points 3 years ago
i signed up at mba.com and it wouldn't let me use a password because it contained a semicolon which wasn't on the approved list of special characters, and then - get this - because I tried too many times to create a password - locked me out because I had "too many failed attempts"
CoderKat 7 points 3 years ago
Those requirements drive me crazy, especially because they're all against NIST recommendations. Someone thinks they make passwords more secure but they have the opposite effect.
At any rate, password managers still help in those cases. If nothing else, for providing a safe place to record what your password is for when you forget it because of the dumb requirements.
setsneedtofeed 4 points 3 years ago
I always wonder if such choices come from incompetent IT, or if IT wants to do things better but is banging their heads against corporate owners who think “more hassle = more secure”.
peto 1 point 3 years ago
It's almost certainly that writing security standards for an organization takes time and needs approval from high up. And someone high up complaining that they only just revised them to include special characters.
mikiao 6 points 3 years ago
Must be changed every month, can't use a previous password, AND, for some fucking reason, can only contain 8 characters.
And if you forgot your password, you can call IT and they'll just read it to you because they have them all saved somewhere.
That was a great place to work at.
setsneedtofeed 0 points 3 years ago path: 0 1288035 1304111 1304372 1304525, hotness: undefined, score: 0, children: 0
confetti_8tVST5 0 points 3 years ago path: 0 1288035 1318244 1320139, hotness: undefined, score: 0, children: 1
Archpawn 0 points 3 years ago
If I'm typing on a computer keyboard, typing words is easier than random letters, but on a phone it doesn't make much of a difference. What I end up doing is typing my passphrase into my password manager on the computer, and then typing the password on there into my phone.
I do have a password manager app for my phone, but then I have to type the whole passphrase into it so I don't use it unless necessary.
SpacedBear 22 points 3 years ago
Looks like someone's been playing the password game https://neal.fun/password-game/
everythingsucks 13 points 3 years ago
That game made me want to punch.
dancing_umbra 13 points 3 years ago
Yeah that really bugs me.
Like come one, "Ma5terp!ece" is more secure than "Regain Refinance Clarify Cuddle9"
Maybe in bizaro world.
MajorHavoc 20 points 3 years ago
I've seen this but with a final message of "Sorry, that password is already in use by user about2getOwned@gmail.com."
StarkillerX42 1 point 3 years ago
- Login to their account
- Change their password to something else
- Set your password
StarkillerX42 0 points 3 years ago
Refer to my above comment until that is no longer the case.
DmMacniel 18 points 3 years ago
A password prompt should include all criteria upfront so that you can setup your password manager to generate a fitting password.
Getting the criteria or even just partial after you entered one is fucking atrocious.
Doug 1 point 3 years ago
Ultimately that makes it easier to break.
How many people do you suppose don't exceed minimum requirements? Once you've got that you can reduce how much you need to generate.
Yeah, you can get that by going to the sign up process, but it generates an extra step that would also increase automation/scraping efforts since it's rarely in the same place.
KairuByte 2 points 3 years ago
It wouldn’t really increase the effort much. A human would have to go through the process once, then just pass those requirements off to the script. The initial setup isn’t something you typically hand off to automation.
Smokeless7048 6 points 3 years ago
i wouldn't even mind if it was 32. 32 is a damn strong password.
I've seen as low as 10 digits in the past
Smokeless7048 1 point 3 years ago
Wow, super secure!
graphite 1 point 3 years ago
32 is a damn strong password
Not necessarily: only if it's generated properly, and only for the moment - that will change in the next few years.
You do realize that length and symbol type are only 2 out of many other factors that go into a strong password?
Smokeless7048 2 points 3 years ago
Ok, fair, not all 32 digit passwords will be secure.
11111111111111111111111111111111 is not secure, but I was trying to imply, in a properly generated password, 32 digits long is very secure.
graphite 1 point 3 years ago
but I was trying to imply, in a properly generated password, 32 digits long is very secure.
I understand, and I think you make a valid point as far as the discussion is concerned.
It's unfortunately still a little more complicated than that, though.
Like I said, there's more to a password than length and symbol type.
Even something like cF*+@aXbIdFHje2vZiU-1 is less secure than if it were generated by a good PRNG.
D0@ndro!dsDr@3@m0f3l3ctr!cSh33p? is also insecure, though it might have been considered secure 4-5 years ago.
You see what I'm saying?
Then of course there's hash algorithms and how those are used to authenticate the passwords themselves, etc.
Affidavit 16 points 3 years ago
Sorry, you must have a special character. Oh... Not THAT special character, it has to be a special special character, that one isn't valid. Ah, no, that one's too long. It should be shorter. It needs to be between 11 and 11.5 characters.
Half the time I now just enter random nonsense until it lets me create an account. Then, when I want to access a website/app again, I just 'forget' my password and reset it to some other random nonsense.
complacent_jerboa 14 points 3 years ago
that password is already in use
lmao, "security" moment
complacent_jerboa 3 points 3 years ago
Large Brian Moment, for real
WagnasT 13 points 3 years ago
My new favorite is the minimum time between password changes. My last 2 jobs set it to 24 hours, so IT guy gives you the temp password and you can't change it for 24 hours. But wait, when you try to change it the error you get is "doesn't meet your organization's minimum complexity requirements" which does not help AT ALL and the IT guy thinks you're an idiot because you can't figure out the complexity requirements. What a great feature!
LaggyKar 11 points 3 years ago
And that's when they tell you what you did wrong. Sometimes they'll reject the password without telling you why, because of some rule they didn't list. For example, I set a password in a parking app (Flowbird) which had an unmentioned restriction against spaces and Swedish letters (dispite targeting the Swedish market). Also, it lets you set a fairly long password, but when you try to log in on their webpage they've set maxlength="32" on the password field. So if you have a longer password you have to edit the DOM and remove that attribute to log in.
corsicanguppy 11 points 3 years ago
I lent my spouse's mother our apple ID while theirs was toasted. But of course I had to change it first, since OhFuckMeH@rd3rYouFucks was finally an acceptable password for Apple but not for in-laws.
ChaoticEntropy 10 points 3 years ago
In what world are passwords unique.
VindictiveJudge 7 points 3 years ago
I did once encounter a site in the early 2000s that wouldn't let me use a password because it was already in use by someone else. I was too young at the time to realize how bad that was, but I remember thinking it didn't make sense.
Tyler_Zoro 7 points 3 years ago
It MIGHT not be as bad as you think. If the UI was just terrible at communicating and what it actually meant was, "that password is in our database of known compromised passwords," then that would be reasonable. Google does this now too, but I think they only do it after the fact (e.g. you get a warning that your password is in a database of compromised passwords).
Trapping5341 4 points 3 years ago
 Can confirm that Google will do this for you. Also, I switched to Bitwarden and Firefox last year so most of these passwords have either been changed or I haven't been on the site in years and don't much care and im not actually this exposed anymore 😂😂
c0mbatbag3l 3 points 3 years ago
The one where LastPass lobbied the government via time travel shenanigans.
Uniquitous 2 points 3 years ago
Within the tiny, circumscribed world of a single instance.
sabaku_no_gaara 10 points 3 years ago
We allow memes here?
ReadyUser31 5 points 3 years ago
Bad memes, too. This is some fwd: fwd: fwd shit.
steal_your_face 2 points 3 years ago
Boomer memes
noodlejetski 0 points 3 years ago path: 0 1263309 1272559, hotness: undefined, score: 0, children: 0
samus12345 10 points 3 years ago
I hate that most places don't remind you what the rules of their passwords are if you've forgotten yours. Odds are I'd be able to correctly guess it if I knew.
LazaroFilm 8 points 3 years ago
HorseBatteryStaple
dancing_umbra 7 points 3 years ago
correct
correcthorsedickbatterystaple 6 points 3 years ago
...so close
be_excellent_to_each_other 6 points 3 years ago
The number of times I've gone through that only to have it fail without explanation when I exceed the length limit - forcing me to guess if that must be the issue - is FAR higher than it should be.
And fuck any system that doesn't provide the criteria up front.
SkadusX 8 points 3 years ago
Also fun is when the field to initially set the password is also character limited and you choose a password that’s longer than the field but don’t notice until you’ve set it and get repeated login failures afterward
TheNH813 7 points 3 years ago
Yeah that nearly makes me want to smash something when it happens. Anyone that silently truncates passwords should NOT do it, or at least truncate the creation AND login forms. Just say the limit and give a error, or handle extra input the way you're supposed to in the enceyption algorithm and hash it to to the correct length. A length limit of say, the amount of bits the encryption key has, like 32/64/128 chracters for 256/512/1024 bit, is reasonable, any other limit is stupid.
be_excellent_to_each_other 3 points 3 years ago
YES, I have hit this too!
ZILtoid1991 6 points 3 years ago
Is there any actual services that check if the password is already in use?
I've heard that some really obscure website even told you who used that exact password, because the CEO of the company owning said website complained for not having it, then the IT company who made the website had to add it. (If you ask: it was some Hungarian-owned website, and not space Karen's 1000IQ idea)
dan1101 4 points 3 years ago
There are definitely services that fuss if you use a password you've used before.
-Try to log in, password incorrect.
-Try to log in, password incorrect.
-Try to log in, password incorrect.
-Weird, ok reset password.
-"Enter new password." Enter the password I've been typing the whole time. "Sorry, you can't use your old password."
-DAMMIT!
I'm pretty convinced this happens because their password validation isn't responding quickly enough and it defaults to "password incorrect."
Uniquitous 6 points 3 years ago
As a sysadmin, can I just say: BAD PASSWORD: more than 3 consecutive characters of the same class
TIEPilot 2 points 3 years ago
My cabbages!
PipedLinkBot 7 points 3 years ago
Here is an alternative Piped link(s): https://piped.video/zRFDr8Vgp_Q
Piped is a privacy-respecting open-source alternative frontend to YouTube.
I'm open-source, check me out at GitHub.
lunaticneko 5 points 3 years ago
That password is already in use by user 'gigachad'.
Fredselfish 4 points 3 years ago
I know the frustration. Fucked up part is that all that crap makes it least secure not more.
silver 3 points 3 years ago
Password1!
It's surprising how many times I have seen this and variations.
The only one that actually reduces security is the length, as it implies it's stored as plaintext.
The rest do improve complexity for cracking.
volvoxvsmarla 3 points 3 years ago
As a hamster enthusiast, I approve of each password provided by this user.
Madbrad200 1 point 2 years ago
My absolute favourite is when your password is too long but they don't tell you that, I guess because they weren't expecting it. It only causes a hitch when you later try to login and it doesn't let you ....
popemichael 1 point 3 years ago
It's best to avoid passwords that include your fetish
If someone gets to know you, they can more easily guess that you're a Hamtaro or Richard Gere fetishist
DeusHircus 2 points 3 years ago
Richard Gere... Lemmiwinks... Lemmy... Oh god, we're all Richard Gere fetishists, aren't we?
daniskarma -2 points 3 years ago
In not that many years password cracking capabilities would surpass any reasonable password length and character combination.
unixfreak -2 points 3 years ago
If a password input form asks any of these questions, consider the website or service compromised right from the beginning. The reason for this, is that it means they are not storing salted/hashed passwords and your password will be stored as plain text on their servers. There's no reason for any limitations on a password. In the event of a breach, your password will be visible in any database dumped by a hack. Always makes me wince when a password form complains about password length, as it really should not matter. When you hash a password, it will be stored in the database at a specific string length;
Eg; using sha-1 hashing:
pass123 = 5f1e04b7fc8d7067346b77bdbb6a4d4f9f4abace28f15c2b265c710b120393b2
password321 = 8852ab05d5b32f9efd3dcbf69edcfd65464e64c8e5e8310239871e02380e81b3
OdinsonThor 13 points 3 years ago
All of those things can be verified before storing the password in any way, encrypted or not, and checking them would be a requisite before storing it.
While it's true that they don't have a significant impact on the hash generated, they make it significantly more difficult for anyone to guess your password. It's much easier to guess password321 than something like Or^9L%u&QQ12XxI@. And that has nothing to do with how the password is ultimately stored.
unixfreak 0 points 3 years ago
Of course, requiring at least one symbol or upper case letter etc is a good idea, along with a minimum length. Many websites won't let you use a password longer than a certain amount of characters. The only reason for that limitation is that they are storing the database field as plaintext, and anything longer will not fit into that column.
unixfreak 0 points 3 years ago
How is it not true? If a site is saying for example, "password must be less than 20 characters" -- that is purely a limitation based on the size of the database field, which you can only assume it's being adding to that field as plain text. A hash will always be the same length and password length would not matter.
PeeJay 1 point 3 years ago
I'll keep my aswer short, but first of all, usually this format enforcement is done on the client before it is ever sent to the backend, there are many reasons to limit the maximum length other than string length limitations on the database ( not that I can think of many actual good reasons).
Second of all, the client should send the actual password to the backend (allowing you validate these same password requirements on your backend), not the hashed password, hashing the password on the client side would be no better than storing the password as "plain text".
And never is the "plain text" password stored in any database, only sent over to the backend and hashed, every time you set a new password, or log in using an existing one.
LeberechtReinhold 4 points 3 years ago
Any site worth its salt (heh) will verify criteria on client for UI reasons, not just in the backend
Pleonasm 1 point 3 years ago
My favorite password is the string "a", but I never get to use it anywhere due to these ridiculous restrictions 😔 Can you tell me which online services you administer so I can sign up for them and enjoy unfettered use of my favorite password?

technology
@lemmy.world
88895
22277
14630
This is a most excellent place for technology news and articles.

Our Rules
- Follow the lemmy.world rules.
- Only tech related news or articles.
- Be excellent to each other!
- Mod approved content bots can post up to 10 articles per day.
- Threads asking for personal tech support may be deleted.
- Politics threads may be removed.
- No memes allowed as posts, OK to post as comments.
- Only approved bots from the list below, this includes using AI responses and summaries. To ask if your bot can be added please contact a mod.
- Check for duplicates before posting, duplicates may be removed
- Accounts 7 days and younger will have their posts automatically removed.
Approved Bots
go to feed...
technology
@lemmy.world
88895
22277
14630
This is a most excellent place for technology news and articles.
Our Rules
- Follow the lemmy.world rules.
- Only tech related news or articles.
- Be excellent to each other!
- Mod approved content bots can post up to 10 articles per day.
- Threads asking for personal tech support may be deleted.
- Politics threads may be removed.
- No memes allowed as posts, OK to post as comments.
- Only approved bots from the list below, this includes using AI responses and summaries. To ask if your bot can be added please contact a mod.
- Check for duplicates before posting, duplicates may be removed
- Accounts 7 days and younger will have their posts automatically removed.
Approved Bots
go to feed...
I too love the Password game! Please save Paul! I truly care about him! ^Truly!^
(Sorry, I sometimes like to post really bad comments...)
save