
Shopping app Temu is “dangerous malware,” spying on your texts, lawsuit claims
2 years ago by Nemeski to c/technology
Yeah, it is. It's such an extraordinary claim.
One requiring extraordinary evidence that wasn't provided.
"It's doing amazing hacks to access everything and it's so good at it it's undetectable!" Right, how convenient.
Libmanwe-lib.so is a library file in machine language (compiled). A Google search reveals that it is exclusively mentioned in the context of PDD software—all five search results refer to PDD’s apps. According to this discussion on GitHub, “the malicious code of PDD is protected by two sets of VMPs (manwe, nvwa)”. Libmanwe is the library to use manwe.
An anonymous user uploaded a decompiled version of libmanwe-lib to GitHub. It reads like it is a list of methods to encrypt, decrypt or shift integer signals, which fits the above description as a VMP for the sake of hiding a program’s purpose.
In plain words, TEMU’s app employed a PDD proprietary measure to hide malicious code in an opaque bubble within the application’s executables
This is why companies like Apple are at least a tiny bit correct when they go on about app security and limiting code execution. The fact it aligns with their creed of controlling all of the technology they sell makes the whole debate a mess, though. And it does not excuse shitty behavior on their part.
But damn
And if they got this past Apple in their platforms. That’s even wilder.
The article linked to the analysis and on a quick glance, it seems to be done entirely against the Android variant of the app. This makes sense because if the alleged actions are true, they’d never have gotten on to the App Store for iOS Apple users… or at least as of a couple months ago. Who knows what kind of vulnerability is exposed by Apple only doing limited cursory checks for 3rd party App Stores.
- Dynamic compilation using runtime.exec(). A cryptically named function in the source code calls for “package compile”, using runtime.exec(). This means a new program is created by the app itself.—Compiling is the process of creating a computer executable from a human-readable code. The executable created by this function is not visible to security scans before or during installation of the app, or even with elaborate penetration testing. Therefore, TEMU’s app could have passed all the tests for approval into Google’s Play Store, despite having an open door built in for an unbounded use of exploitative methods. The local compilation even allows the software to make use of other data on the device that itself could have been created dynamically and with information from TEMU’s servers.
Ah yes, delete your original incorrect comment instead of continuing the discussion about how wrong and lazy it was to make, nice.
I'm sure Temu collects all information you put into the app and your behaviour in it, but this guy is making some very bold claims about things that just aren't possible unless Temu is packing some serious 0-days.
For example he says the app is collecting your fingerprint data. How would that even happen? Apps don't have access to fingerprint data, because the operating system just reports to the app "a valid fingerprint was scanned" or "an unknown fingerprint was scanned", and the actual fingerprint never goes anywhere. Is Temu doing an undetected root/jailbreak, then installing custom drivers for the fingerprint sensor to change how it works?
And this is just one claim. It's just full of bullshit. To do everything listed there it would have to do multiple major exploits that are on state-actor level and wouldn't be wasted on such trivial purpose. Because now that's it's "revealed", Google and Apple would patch them immediately.
But there is nothing to patch, because most of the claims here are just bullshit, with no technical proof whatsoever.
The study and evidence was already provided months ago
https://grizzlyreports.com/...
This was also linked in the article if you read it
Here's the actual relevant part
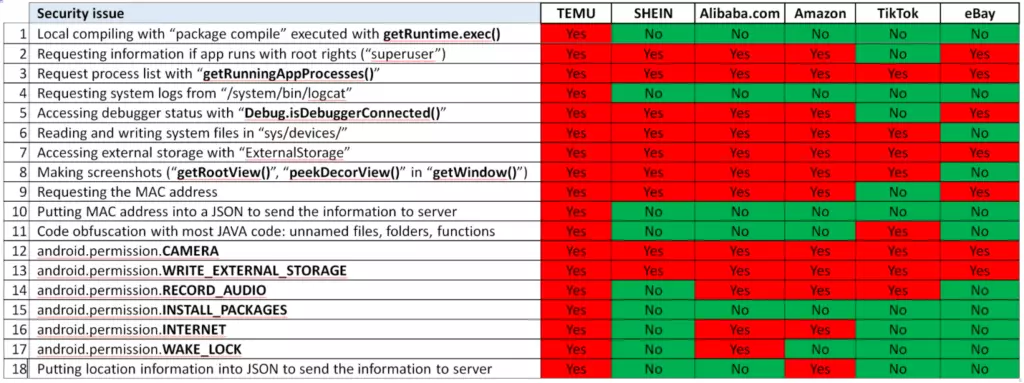
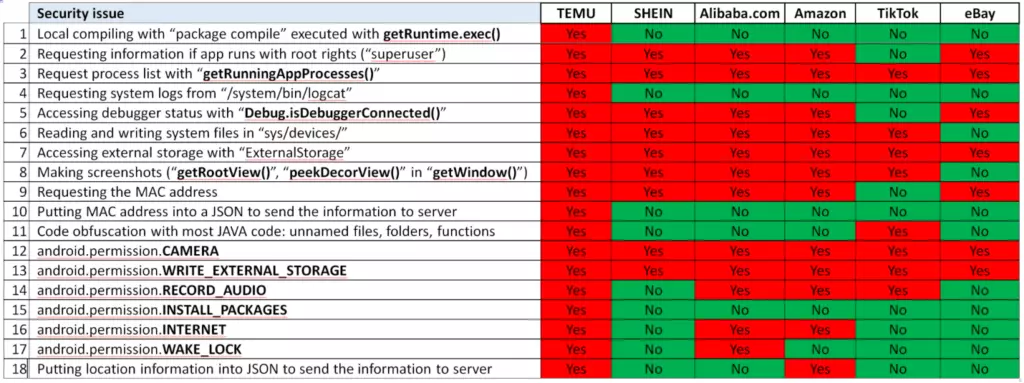
These are security risks to be sure, and while these permissions are (mostly) on the surface, possibly defensible, together they do clearly represent an app trying to gather all of the data that it can.
However, a lot of info from this report is overblown. For example code compilation is sketchy to be sure, but without a privilege escalation attack, it can't do anything the app couldn't do with an update.
Also, there's some weird language in the report, like counting the green security issues in other apps (like tiktok) as if they were also a problem, despite the image showing that green here means it doesn't present that particular risk.
All of this to say, if you have temu, probably uninstall it. It's clearly collecting all the data it can get.
But it's unlikely to be the immediate threat that will have China taking over your phone like this report implies.
I'm blown away by how many people use apps when they don't have to. There's a reason companies are always trying to get you to download their app, and it's so they can put their software on your phone and harvest more of your data.
Exactly why I use browser and not apps, too. and if they try to strongarm me with better prices or degraded services, I just stop using them all together.
Thanks, that brings done useful context here
That.. is not a study by anyone who knows what they are talking about. It also does not mention fingerprints at all.
They seem to believe that the app can use permissions undeclared in the manifest file because they obviously think it's only for the store to show the permissions to the user. Android will not actually allow an app to use undeclared permissions. The most rational explanation is the codebase is shared with different version of the app (possibly not released) that had different manifests.
It also makes a big deal of checking if running as root. That is not evidence of having an escalation exploit. If they have an ability to get root before running the app why would they need to use the app to exploit it? They could just do whatever they wanted and avoid leaving traces in the app. Though I doubt they would root phones to just brick them. It's the kind of mischief you would expect from a kid writing viruses, not an intelligence agency or criminal enterprise.
Users who root their own phones are very unlikely to run temu as root. In fact a lot of apps related to shopping or banking try to detect root to refuse to work as your system is unsafely. In any case it's a very niche group to target.
To keep things short, that 'study' does not really look credible or written by actual experts.
The article links to this as technical proof https://grizzlyreports.com/...
There's analysis of decompiled source code.
The analysis shows it's spyware, which I don't question. But it's spyware in the bounds of Android security, doesn't hack anything, doesn't have access to anything it shouldn't, and uses normal Android permissions that you have to grant for it to have access to the data.
For example the article mentions it's making screenshots, but doesn't mention that it's only screenshots of itself. It can never see your other apps or access any of your data outside of it that you didn't give it permission to access.
Don't get me wrong, it's very bad and seems to siphon off any data it can get it's hands on. But it doesn't bypass any security, and many claims in the article are sensational and don't appear in the Grizzly report.
That is not entirely correct. The reported found the app using permissions that are not covered by the manifest. It also found the app being capable to execute arbitrary code send by temu. So it cannot be clearly answered if the app can utilize these permissions or not. Obviously they would not ship such an exploit with the app directly.
The reported found the app using permissions that are not covered by the manifest.
It didn't found them using them, it's an important distinction. It found code referring to permissions that are not covered by the Manifest file. If that code was ran, the app would crash, because Android won't let an app request and use a permission not in the Manifest file. The Manifest file is not an informational overview, it's the mechanism through which apps can declare permissions that they want Android to allow them to request. If it's not in the Manifest, then it's not possible to use. It's not unusual to have a bunch of libraries in an app that have functionality you don't use, and so don't declare the required permissions in the Manifest, because you don't use them.
It also found the app being capable to execute arbitrary code send by temu.
Yeah, which is shady, but again, there is nothing to indicate that code can go around any security and do any of the sensational things the article claims.
The Grizzly reports shows how the app tricks you into granting permissions that it shouldn't need, very shady stuff. But it also shows they don't have a magical way of going around the permissions. The user has to actually grant them.
Do you know if there people who have gone this far analysing the TikTok and WeChat apps?
Haven't read the article because I'm not interested in an app I don't use, but does it mean browser fingerprint? Because that's slang for the fonts/cookies/user-data of your browser, and lots of apps have access to that.
Wouldn't the phone have to have your fingerprint stored in order to compare it to the one scanned?
Yes, the phone does, but that data is protected in the hardware and never sent to the software, the hardware basically just sends ok / not ok. It's not impossible to hack in theory, nothing is, but it would be a very major security exploit in itself that would deserve a bunch of articles on it's own. And would likely be device specific vulnerability, not something an app just does wherever installed.
Temu is absolute cancer in terms of business practices so no surprise here at all.
Cancer in terms of, well, everything.
But it's cheap.
Why is Temu so popular then?
Because people get dopamine from shopping, even if it's garbage. It causes enormous amounts of waste, because most of the crap isn't used much if at all. They just make it look good on the product page.
How about pass and enforce strong digital privacy protection laws you fucking cowards. When other countries spy on us it's scary and bad, but for US companies? Best we can do is ban porn and demand backdoors to stop E2EE messaging.
California (and a few other states) are trying. The CCPA and CPRA are a good step in the right direction. If you're a California resident, you can request all the data a business has collected about you, tell them to stop sharing it with business partners, or tell them to completely delete it, similar to the GDPR in Europe.
Oh don't worry, they're going to try and kill that too before it hurts them too much, and with the audacity of calling it the "American Privacy Rights Act". https://www.eff.org/...
Unfortunately they care more about spying on us themselves.
That would hurt the advertising, spam, blackmail, malware, and propaganda industries. We can't rip out the economic spine of big tech since they pay the best bribes.
Plenty of items on eBay are just people who buy from China directly and mark up prices. If it is likely made in China and I don’t want it quickly, I’ll buy off aliexpress. That said, alibaba wanted me to upload photo ID which I noped out of. Temu started spamming my email address when I’d never used them. The unsubscribe link went to their website said to adjust your account settings if you didn’t want spam… I never created and account and avoided them completely following that.
Amazon is usually OK if you buy things that are sold by Amazon or sold by the manufacturer (if it's a well-known brand). The third-party sellers on Amazon based in China are almost always reselling stuff from Aliexpress/Alibaba with a significant markup.
Half of them aren't in China though. It's dropshippers, so you still get your cheap death traps, but you get them in a few days, Amazon get their enormous cut, and they get to take no responsibility when it burns your house down.
I don't buy anything from eBay that I can get elsewhere. I didn't even use those other sites. Sure, everything is made in China, but I'm good not trusting China without a more reputable middleman that's subject to American laws regarding things like refunds and such.
Alis search is really bad.
Somehow the auto translation is active for the product names but if you search they don't seem to apply.
For example:
Searching for Cherry MX switches brings up articles that are named "Mechanische Kirsch Schalter für Tastatur" (essentially the name but translated). Problem is: Cherry the company is like it's in english as well, also the fruit amd thus will not be translated correctly.
Trying to search more niche stuff quickly gets annoying when trying to find something specific.
somethings people don't care about quality. An example, the one time I checked out Temu way back when it first made its splash I bought some targets for shooting... Hard to fuck that up and got em cheap as fuck with that promo deal they do to hook you. Uninstalled it right after, probably not worth it but I feel like that is a common experience. There are items where you just simply can't fuck up so the ultra cheapness works out.
With that said, an obligatory FUCK temu and those like it.
They don't seem to give overall preference to a given supplier beyond their obvious coupons and paid rankings. Alibaba is better, but who needs 144 of any specific widget..?
If you compare to one of the most preferred e-commerce website, which I would consider Amazon, it's still not that bad. I have found less lies on Ali express v Amazon. If it comes to any cheaper electronics the Ali description is the real deal as far as I have seen. Amazon I have been shipped differing products, the description or features have just been a lie, or it didn't come with the things implied. For the most part Ali descriptions are exactly what you will expect when opening the product... in fact many times I discover extra features when receiving the product that seemingly just couldn't explain in their marketing.
Ali>Aliexpress>Amazon... just depends on needs
My only reasons to buy on Ali is when I need something simple like velcro that can be cut to length or other small scale stuff electronics (e.g. Rasperry Pi 0) and it doesnt have to be fast.
Ironically the shipping is either free or so cheap it's better than domestic amazon.
I often suspect they sell the same item but order it with DHL shipping (our domestic shipper) with high priority shipping included in the price (2€ item + 8€ shipping = 10€ on Amazon + "free" shipping)
A huge amount of products are just generic Chinese products that have a brand slapped on it. If you've ever bought a random small USB device (i.e USB hubs, etc) from a major brand like LogiTech and others, if you crack it open it is just the same device as cheap resellers with a branded coating. It's not worth it to many companies to bother manufacturing their own small tat so they just sub-contract out.
And sure, it likely works, but it's the exact same hardware with the same capabilities as a product a 10th of the price.
The cheap Chinese stuff often uses knock-off ICs tho.
They can be fairly difficult to detect, and will work for a short time or under very light loads. But they will be nowhere near the spec of the data sheets.
They might massively overheat, not provide the correct currents or voltages, run at lower speeds. All sorts of corners being cut to turn a $2 IC into a 50¢ IC. Or a 50¢ ic into a 5¢ one
So yeh, might be the same PCB layout inside, it might visually look the same (or very very close) but the parts are likely to be counterfeit.
Of course, it's also probable that name brands might be hit with counterfeit parts inside as well. Hopefully their QA picks that up
I've found this when trying to get a decent USB>9-pin Serial connector.
You think it's your software, or something weird going wrong. Then you swap over a name-brand adapter, and the thing just works.
Yeah, the small tat items and accessories, as I said.
That’s all online shopping
I can't believe people pay full price on cheap stuff. The only reasonable thing to do is pay cheap on cheap stuff. And the delivery times are unbeatable .
I can't believe people buy cheap trash that would be sold on Temu.
But here we are, people buy cheap ass trash off Temu. If China started picking through the trash we shipped them and sold it back to us on a site like Temu, something tells me people would still buy it.
People would buy an actual turd on temu if it's cheap enough. Just read these comments here... But it's cheap. Congrats, you bought cheap garbage and it got send around the globe by a company that sells your data
With how cheap they are, people will and should buy from TEMU. Aliexpress as a general store never had much of a competition for English speakers outside of Banggood for select electronics. Taoboa is good but it's harder to use
So for you, the lowest price is the only thing that matters? It doesn't matter whether it's a shitty product? Or that they're one of the least efficient shippers due to their tariff avoidance strategy, and in doing so are contributing more per purchase to climate change than even companies like Amazon and Walmart?
I'm assuming you don't own a smartphone, because many of those materials are extracted by exploiting the local populace in Africa
I'm happy because it's competition for Aliexpress.
Arguments against carbon emissions and carbon footprints against corporations isn't very helpful unless you can do something about it. This is somehow a very unpopular opinion here, for some reason people don't like being told that they don't have much power. Boycotting it by yourself won't work either, because even if the west gives up on it, the East will not. Carbon emissions will remain unless strict regulations are maintained, and we know who buys politicians these days. If I can do nothing about the climate, then yes I'd rather pay less. And I'm not explicitly anti-China like some people here because America is just as hypocritical.
Yes there are really bad products and their QC is horrible. I'll say the same for Aliexpress, Taobao, Amazon, Walmart and Bestbuy. Unfortunately for everyone here, we're going to have to choose between shit options, so yes I'd rather pay less if it's shit I'm going to get anyway. Besides, I'm smart enough to not make bigger purchases on these sites because I know of their QC situation.
Boycotting is a collective action, it spreads like a virus, so you are wrong on its effectiveness.
You sound like someone who wants hand waive away the real costs of their actions by saying there's nothing you can do to change things.
I hope the people who read your post aren't demotivated to effect change because of it.
Yes there are really bad products and their QC is horrible. I'll say the same for Aliexpress, Taobao, Amazon, Walmart and Bestbuy.
There's a huge difference between some 5/10 products at Walmart and Best Buy and the best case being a 5/10 product with the majority being 2/10 and some being actually dangerous like Temu.
They're not remotely similar.
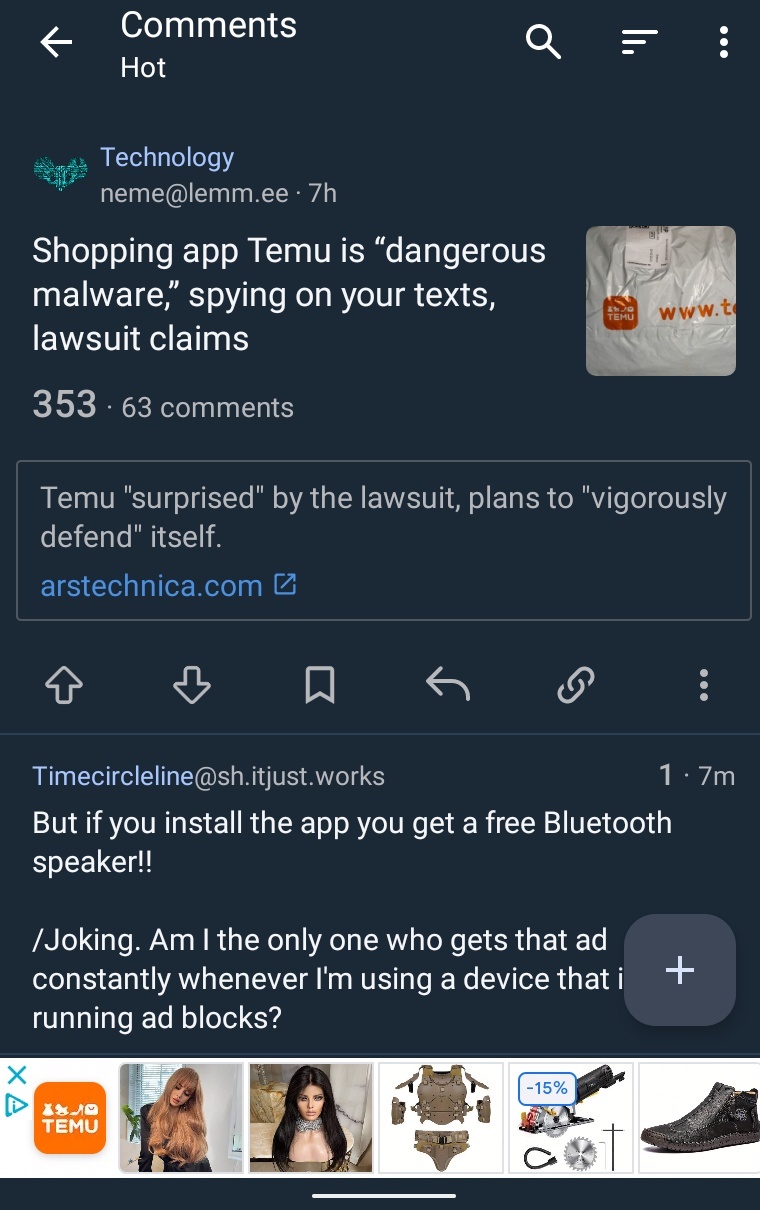
The irony
First, you use Lemmy, that's great. But pls use a client without ads....
Been using Boost since it was a Reddit client. By default, it is my go to.
Maybe but you've done the transition to Lemmy try to use a libre client
I'm all for Libre but in this case @rmayayo@lemmyworld is my leader.
by "client" do you mean "just use a browser"?
Or, you know, the 98% of clients that don't have ads. I, for one, recommend Voyager.
Maybe but not only, for phone I recommend an app that's much more optimized for using on mobile
Lemmy website is fine on mobile imo. Not perfect but usable and optimized.
Bro why using Lemmy if it's for using proprietary client? Voyager, Jerboa, you have others choice...
Where are you viewing Lemmy posts that you have ads?
I’m using Voyager and it’s great. I don’t even use the app, I prefer the PWA.
I also use Voyager and agree, plus it’s actually open source.
I see; I can’t imagine willingly submitting to ads, but whatever works for them.
Yeah. Boost itself is great though. Well worth the couple of bucks to get rid of the ads forever.
I use it too. Tried a few different ones and like boost the best. I finally just paid for the non-ad tier. One time cost of 3.99. I would have been turned off by a subscription.
Yeah boost is definitely good, it was my main app until a few months ago. Recently I have been trying Connect, which is another great app.
Connect has improved a lot since I first tried it, also doesn't have any ads. But all things considered - Boost is bit more polished than connect.
That's what you get for using a proprietary Lemmy app. Switch to Thunder, it doesn't have ads, it's open source and in my opinion has the best UI out of all Lemmy apps. Also support the development and join their community: !thunder_app@lemmy.world
Jerboa here but same
I tried using Jerboa and found it to be incredibly buggy and poorly designed. Not sure what's going on there, considering that it's the official mobile app made by the Lemmy devs
Has worked mostly fine for me, YMMV
Lol
I generally think arstechnica.com does a decent job of being a non-garbage news site. I pay a couple bucks a month for the ad-free RSS feed. This story feels terrible to me. I don’t doubt a law suit has been filed, but I would expect some investigation by the reporter of the extra-ordinary claims of privilege escape the application is claimed to be capable of.
Given that the headline says that it is a claim in a lawsuit, and the lawsuit is by a state attorney general and not some random nobody, I feel like they are being fairly reasonable.
I would feel that it would be a reasonable if it was my local paper running the story. Arstechnica IS a primarily technical news site—I believe they should have a higher bar—otherwise they are just parroting a report and not providing useful (to me) news.
What about Meta and Google?
it doesn't count when it's an american company doing it
Erm, WhatsApp would suggest otherwise.
WhatsApp was the vector for zero click access to a target's phone from Israel's weapons grade hacking Pegasus toolkit. They would send a video call, typically in the middle of the night, and with no input from the used they'd get full access. My personal belief is that they used functionality WhatsApp itself uses to access user data.
There was also an encrypted phone called ANOM, which had this trick calculator app with a hidden encrypted messager. "Made for criminals, by criminals". Except, when the guy started his business he got investment from the FBI and Australian Federal Police to pay for the servers and some of the phones themselves. Basically every time it sent an encrypted message it sent a separate encrypted message to the ANOM servers. It's entirely possible (perhaps even likely) that WhatsApp would do this also.
As for Google, they're truly insidious. Lots of banks now require you to connect to Google captcha servers - they don't give you the pictures, it's just the back end, basically the tracking parts. Then there's the controversy about them collecting location data when users have said no. They absolutely do collect data they shouldn't.
I'll accept that maybe I'm giving Google a pass because of misplaced nostalgia, and while I personally have never used or liked Meta Facebook, I'll concede that for a while it provided a service some people valued.
It's still my opinion that Google and Facebook have a large percentage of engineers that personally try to make them a genuinely good service, at least moreso than compared to TikTok and Temu. But I'm willing to concede it's not as much a practical difference as I would like.
Why do you say that?
Cause they are owned by American billionaires and as such are more ethical. /s
Emphasis on by comparison, as in "molten hot metal is cooler than the surface of the sun, by comparison".
TikTok and Temu actively have code in them that would be considered a virus in other contexts. They exploit your system to gain more access than they should, violating the point of sandboxed access.
By comparison Meta and Google merely take advantage of user ignorance and apathy by making opting out frustrating - but still technically doable.
Both practices are terrible, but that's not the same as saying they're equally bad.
Have any of you actually ever stopped to process what the tagline, "I'm shopping like a billionaire" means?
I've always interpreted it as,
I'm needlessly buying things that don't make me happy, but making the purchase without any hesitation, knowing that the purchase price could never financially impact me in any real way. When I purchase the thing, I'll probably never use it or actually take it out of the box even. It is just empty, hollow. And somewhere inside, I always know that it's all only possible, because I'm actively exploiting the cheap labor of scores of other people that are made to perpetually suffer in generations of abject poverty to allow for my relative comfort...
🎶*"I'm shopping like a billionaire!"*🎶
I am disabled and have limited income I don't have control over increasing or decreasing. I use temu to save a lot of money on essential things that should be cheap but are still overpriced in America. Sponges. Rags. Soaps. Pens. Tools. Home improvement hardware. Plant grow supplies. Gifts for me nieces. The tagline, is just a tagline. Billionaires are not like me and scouring for cheap magic sponges.
Edit: also, temu did not invent drop shipping. Shopping on amazon is literally the same thing.
Good to know people that are disabled don't mind using shitty maleware apps, I guess?
What's your point combining using the malware app with you being disabled? Is that supposed to make the app better somehow?
You're not special because you're disabled. Things you use aren't magical amazing. You're still the same as everyone else.
That's... not what they were saying? They were responding to a comment saying it encourages consumerism by saying that they use it for better prices on things they need regardless
What does being disabled have to do it?
Well this disabled person thinks you're a dumb asshole.
For what reason exactly?
All I want to know is what do these Temu people think my life is like?
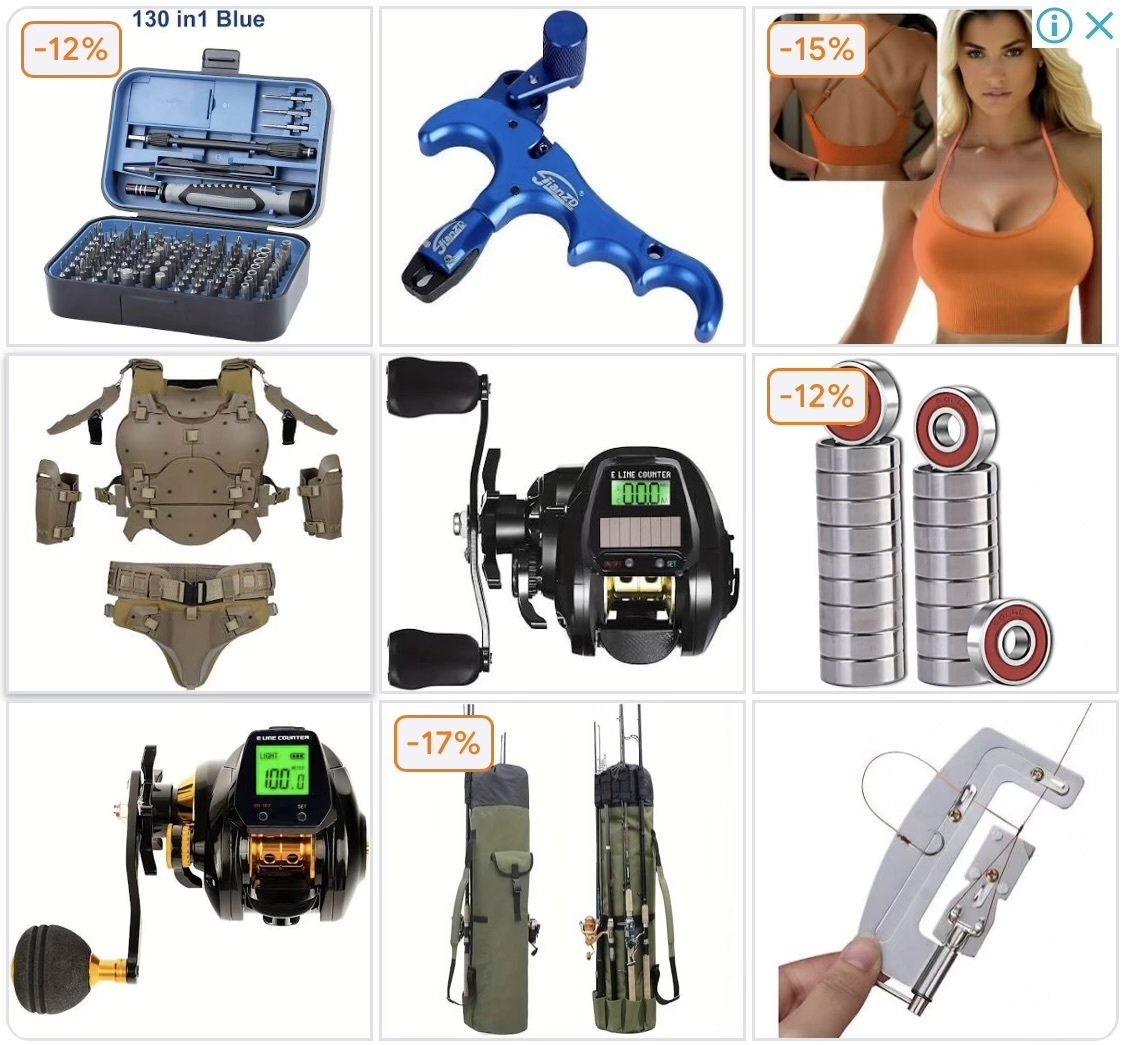
Are you a busty outdoorswoman?
I mean, you're obviously a sexy military mechanic woman, who goes into battle with fantasy battle armor and goes fishing as a hobby! Duh.
Trust me, fish dont need to be robots to be fucked....
I was wondering what that blue thing was. I thought it was a weird personal tool....
Weaponized fishing for covert military operations.
Clearly you use adbloker or something cause temu just got excited when you opened up the link.
he's batman
Batwoman
No, you don't get it.
These massive Batman pecs need support.
Bustybats
Yesterday, I saw a Temu ad for something and I just wanted to open it to read the info and there were so many popups and "spin the wheel for a prize" and "enter your email here" and so on that I gave up and just looked for the info elsewhere. Never clicking on a Temu link again.
Same, but a year ago.
Also, Temu has tried to take all the shopping search results from Bing/DDG. So those results are trash now.
I get their CAPTCHA where I have to slide the puzzle piece over to look at one of their ads. More than half the time I will do this and it will fail saying I didn't do it right. So yeah temu has become a trash site.
one of the best decisions you'll ever make, next to dns level blocking it on your network.
I'm shocked, I say. Shocked!
The idea of an app being used to gather additional datea from a customer!
Comments here: “Yeah right, I’ll believe it when they explain how.”
Article: literally has a section explaining how
Edit:
Replies: "Yeah, but that's just a summary. I'll believe it when they explain in full detail."
Article: literally has a link to the detailed explanation
The claim is they completely bypass all Android and iOS security is pretty unbelievable.
If so then the real discussion is how these zero day exploits are just sitting around.
EDIT: It seems the focus is on Android but all the information is nonsensical, like AI generated buzzword bingo.
I'm not seeing too many buzzwords here
That source looks better indeed.
Ars quotes nonsense like “bypasses the security” and “exploit the user”.
Those terms have meaning and they aren’t applicable here.
At the end though they do say things like
is able to hack your phone from the moment you install the app
Without any credible evidence.
It states that it’s somehow breaking the permissions sandbox by dynamically recompiling code after the app is opened. Unless there is some undisclosed exploit that it’s using to break the sandbox, it’s outside most people’s understanding of how these platforms work
Someone else posted this report in this thread which does a good job of the deceptive practices and API calls the app uses to trick the user into giving permissions up willingly and otherwise collect data it shouldn’t.
That's also most of what's on Amazon these days.
Amazon is just faster shipped temu garbage
Every person I've heard hate on temu shops on amazon, too. It's pretty ironic.
If it’s $5 and some random assortments of letters for a brand name you might as well just light your money on fire whether you order from temu or amazon or Walmart for that matter
Can someone explain to me how you can just simply program something to bypass privacy and security features? What is the point of having these features if you can literally just program something to ignore them? Like....??? Temu is obviously bad if this is true, but if it IS true, it shouldn't have been possible to begin with!!
Im not sure how they specifically bypass the features in other ways but I imagine some of it is from users accepting permissions under the guise of another use. For example, maybe you accept the microphone permission on tik tok to record video. With that permission in theory the app could now use it maliciously. Of course it should all depend on the users choice for that and im not sure beyond the scope of that.
TORfdot0 shared this comment below:
Someone else posted this report in this thread which does a good job of the deceptive practices and API calls the app uses to trick the user into giving permissions up willingly and otherwise collect data it shouldn’t.
By exploiting unknown vulnerabilities in the operating system.
Looking forward to someone answering this
one of the most obvious ways is to simply not bypass them, and then do it from within the application itself. That way you can essentially man in the middle the rest of it, though this would require a rather specific set of events and a particularly nested design of an app.
Same like wish
Shop like a billionaire targeted by state sponsored hackers.
Not enough just to get someone else to take your cheap plastic shit to landfill after it's cluttered their space then I guess.
But if you install the app you get a free Bluetooth speaker!!
/Joking. Am I the only one who gets that ad constantly whenever I'm using a device that isn't running ad blocks?
since people are yelling about it.
It's probably not blatantly bypassing security and privacy features, what it is PROBABLY doing is using the user to bypass them by simply manipulating them to do it.
Social engineering is way easier than whatever bullshit you would need to do to bypass sandboxing and dynamically recompile, or whatever people are claiming, and my guess would be that this is what they're doing.
If the suit is claiming they are doing what i said, that's probably legal, and not going anywhere, unless tiktok ban bill 2.0. If the suit is claiming what others are claiming, it's still probably wrong and probably going to be tiktok ban bill 2.0.
Unfortunately these things aren't all that exciting at the end of the day.
Friendly reminder to ,check out Friendly Social Browser to get all these apps in a better experience and secure/private context
Probably when the software isn't malware.
But in this case it is.
The 'But, everyone is a bit evil' argument is such bullshit, the concern here is obviously the extent of the surveillance, but no one can say you're entirely wrong because the definition of that is so broad.
It's kind of technical, but there are comparisons on the report itself, even a fancy table, to other popular shopping apps and there are some legitimately troubling items. For anyone else, I'd recommend skipping direct to the source:
There wouldn't be so much anti-china propaganda, if the popular companies didn't do so much shit behind people's back to drown out the good things coming out of China.
I mean China is becoming a economic powerhouse, just make your companies not be backdoors until your influence and trust increase without competition. But nooooo, they have to do every worse thing other big tech companies do, but at a script-kiddie level.

@lemmy.world
This is a most excellent place for technology news and articles.

Our Rules
- Follow the lemmy.world rules.
- Only tech related news or articles.
- Be excellent to each other!
- Mod approved content bots can post up to 10 articles per day.
- Threads asking for personal tech support may be deleted.
- Politics threads may be removed.
- No memes allowed as posts, OK to post as comments.
- Only approved bots from the list below, this includes using AI responses and summaries. To ask if your bot can be added please contact a mod.
- Check for duplicates before posting, duplicates may be removed
- Accounts 7 days and younger will have their posts automatically removed.
Approved Bots
go to feed...
@lemmy.world
This is a most excellent place for technology news and articles.
Our Rules
- Follow the lemmy.world rules.
- Only tech related news or articles.
- Be excellent to each other!
- Mod approved content bots can post up to 10 articles per day.
- Threads asking for personal tech support may be deleted.
- Politics threads may be removed.
- No memes allowed as posts, OK to post as comments.
- Only approved bots from the list below, this includes using AI responses and summaries. To ask if your bot can be added please contact a mod.
- Check for duplicates before posting, duplicates may be removed
- Accounts 7 days and younger will have their posts automatically removed.
Approved Bots
go to feed...
That's just nuts
save