
Edit: @Successful_Try543@feddit.org solved it. It says "one special character". Not "at least one".
Can somebody solve this puzzle?
2 years ago by sorter_plainview to c/programmer_humor
sorter_plainview 90 points 2 years ago
Their desktop site is even more shitty. It won't allow right click or paste actions. There goes compatibility with password managers.
Appoxo 17 points 2 years ago
And even if theres an app for Windows (https://github.com/jlaundry/TypeClipboard) that can type it for you and even has a shortcut.
I am sure someone in the linux world knows an equivalent tool.
We use it at work to paste long passwords when remoting in.
xmunk 38 points 2 years ago
As a super secret dev hack may I introduce you to shift + insert a fair few sites specifically block ctrl + v instead of properly disabling the clipboard action and, of course, if you read this and then submit a Jira ticket to block shift + insert... well... h8u
LuycYQ2uUiTjR3yLri 21 points 2 years ago
You can also drag the password in from another text field instead of pasting
independantiste 14 points 2 years ago
I usually to in the developer tools and manually disable the thing preventing the paste action. It's usually a string to remove some JS or something or an Event that you need to uncheck
sorter_plainview 6 points 2 years ago
Aah.. I completely forgot about that. Will try next time. Also yesterday I saw Shift + F10 will show the context menu. Yet to test it on this site.
Creat 17 points 2 years ago
Any password manager should be able to "type in" the password. Or be a browser plugin that doesn't rely on copy pasting, but use other mechanisms to inject it directly into the field.
But yes, if that's their online portal, I am not kidding I would change banks.
stealth_cookies 32 points 2 years ago
My bank's password used to have to be exactly 6 characters, no special characters and you could use numbers and letters interchangeably because it was also your phone banking password.
hushable 43 points 2 years ago
a previous bank used to have a max password length of 8 characters, then proudly announced that they will increase it to 32
Then I made a typo at the end of my password and it let me in anyway, and I realised they were just trimming the first 8 characters to give the illusion of security
Wizard_Pope 15 points 2 years ago
That is so insane. To think they would rather just clip the passwords instead of habing it be longer.
Did you try out your hypothesis by using the first 8 letters than just random junk until you hit your password length?
hushable 16 points 2 years ago
I tried then first N characters of my password until I found out the threshold was at 8, then I tried with the first 8 chartacters of my password and then random junk and it worked.
I also had two friends in the same bank to validate
DudeDudenson 26 points 2 years ago
Visa has a hard limit of 8 and requires the first 4 to be numbers because the phone tree might require it as a password
The whole banking industry is ridiculous and is ridiculously legislated
funkless_eck 6 points 2 years ago
USAA has 8-12 ONLY. My smallest memorized password algorithm is 13 characters, that I typically use for throwaways, doesn't even fit.
ImplyingImplications 12 points 2 years ago
I had to create an account on a government website. The website didn't list a character limit so I used a password manager to generate a 32 character password. My account was created but I couldn't log in. I used the "forgot my password" option and I received an email of my password in plain text. I also noticed why I couldn't log in. The password was truncated to just 20 characters. Brilliant website! Tax dollars at work!
kirk781 8 points 2 years ago
Some internet banking sites give access after only asking for login password. They will only ask for transaction password and OTP (that will only come on phone) later on. Asking for two passwords isn't necessarily more secure since many people will just reuse their original one again. And OTP instead of offering something like hardware security key is insane.
IsoKiero 5 points 2 years ago
My bank uses 6 digit 'customer number' (which is set by the bank) and that's verified with an app and a personal PIN (app shows 'login attempt ABCD at mm.dd. hh:mm' where ABCD is shown on login page too) or via SMS OTP (again with 'ABCD' verification). And again with personal pin + app or OTP to confirm transactions. The app itself can be protected with a fingerprint or phone pin and every new installation needs to be registered to the system, so I can't just use my phone app to access my wifes account (or anyone elses) but I still can map multiple accounts (like corporate ones) to the same installation.
I think that's pretty reasonable approach.
FiskFisk33 3 points 2 years ago
seriously, I've never seen a bank with password login to begin with. Every bank i know of uses physical devices that you type a code into
WalrusDragonOnABike 7 points 2 years ago
Never heard of this. Where is this at? :o
FiskFisk33 9 points 2 years ago
Sweden. The little keyfob thingies have been the thing for many decades here, I would guess ever since the dawn of internet banking, but I'd have to ask my parents instead of just assuming. I used to assume that was just normal for banks in the world at large. When you want to log in, the website gives you a code, you type the code into the fob and it responds with another code you type in to the website.
Nowadays they additionally offer login via BankID, a mobile app used throughout Sweden for personal online identification.
Successful_Try543 8 points 2 years ago
As a German, when living in Sweden, I was (and still am) very impressed, how widespread the use of (Mobile) Bank ID, beside the use of the personal ID number (As a male German, the state has assigned me at least three different ones without requiring any interaction.) for basically everything, is.
In Germany, before introducing a second electronic way of authentication for online (or phone) banking, it was done by a chosen password and a TAN (transaction number) from a list that you regularly got sent by mail in a special envelope. Later it was replaced by that "thingy", a mobile TAN generator, or push TAN via SMS.
Wizard_Pope 4 points 2 years ago
I want this so bad now.
WalrusDragonOnABike 3 points 2 years ago
OTP for 2FA has just started becoming common here (US) within the last decade I think. Each bank has its own separate app and many banks seem to limit password lengths to less than other websites.
rtxn 5 points 2 years ago
Time-based one-time passwords. It's been used for years for multi-factor authentication.
Successful_Try543 4 points 2 years ago
At least it should not, in many countries must not, be the only measure.
I once encountered an OR in the requirements: Capital letters, small letters and digits OR special characters.
Successful_Try543 120 points 2 years ago
It says one special character, not at least one. Maybe the password has more than one.
sorter_plainview 100 points 2 years ago
Holy shit!! You did it. I would never expect a banking password to max special characters. I have been scratching my head with Bitwarden and this shitty app for an hour.
FederatedSaint 47 points 2 years ago
But wouldn't that mean the bottom checkbox should be cleared and the 2nd one should be checked?
Still doesn't make sense.
sorter_plainview 23 points 2 years ago
Yeah that's true. The UI does not accurately represent the validation conditions.
independantiste 7 points 2 years ago
And the wording is fucking terrible as well
tooLikeTheNope 17 points 2 years ago
Yeah but It still states "A combination of letters, digits and special charaters"
It should then be spelled as "A combination of letters digits, and one special character"
kionite231 10 points 2 years ago
You solved the puzzle! here is a cookie for you :D 🍪
Successful_Try543 2 points 2 years ago
Yay!
brbposting 4 points 2 years ago
Good catch.
Also psh, there’s no verb, suggesting the password should be exactly one special character and nothing else.
xoggy 61 points 2 years ago
That programmer has obviously been playing https://neal.fun/password-game/
AbsoluteChicagoDog 6 points 2 years ago path: 0 12259597 12260009, hotness: undefined, score: 6, children: 2
CheeseNoodle 2 points 2 years ago
I can never get past the geoguesser part
chiliedogg 3 points 2 years ago
Last time I got pretty deep in, but it became impossible when the chess notation rule required Cs and Ds, making it impossible to stay below the roman numberal sum limit.
veloxization 2 points 2 years ago
I got past it because it happened to throw a place from my country. And there was also a flagpole with a flag on it to really drive it home. XD
WhiskyTangoFoxtrot 3 points 2 years ago
No Homers.
Buddahriffic 12 points 2 years ago
Once upon a time, battle.net passwords weren't case sensitive. I used upper and lower case letters in my password then one day realized I didn't hit shift for one of the caps as I hit enter out of habit, but then it still let me in instead of asking for the password again.
It was disappointing because it takes more work to remove case-sensitivity than to leave it. I can't think of any good reason to remove it. At least the character limit had a technical reason behind it: having a set size for fields means your database can be more efficient. Better to use the size of a hash and not store the password in plaintext, so it's not a good reason, but at least it's a reason.
lud 12 points 2 years ago
It's possible that the passwords want through an old ass cobalt system or something that forced everything to be capitalized so to solve that they made everything non case sensitive.
But even that sounds insane as the passwords should have been hashed.
NotAnonymousAtAll 7 points 2 years ago
At least the character limit had a technical reason behind it: having a set size for fields means your database can be more efficient.
If that is the actual technical reason behind it, that is a huge red flag. When you hash a password, the hash is a fixed size. The size of the original password does not matter, because it should not be stored anyway.
Buddahriffic 3 points 2 years ago
Correct, hence the sentence after the one you quoted :)
If any service can recover your password and send it back to you rather than just resetting it for you to set a new one, don't rely on that service for anything you want to keep secure. And certainly don't reuse a password there, though you shouldn't be reusing passwords anyways because who knows what they are and aren't storing, even if they don't offer password recovery.
NotAnonymousAtAll 3 points 2 years ago
Sorry, didn't want this to look like an attack or disagreement. Just wanted to highlight that point, because arbitrary maximum sizes for passwords are a pet peeve of mine.
Matriks404 21 points 2 years ago
Your Internet Banking Password should one special character (~!@#%^&*)
Great grammar on their part.
WhiskyTangoFoxtrot 9 points 2 years ago
Yeah, they noticed their mistake too late, hence the expletive.
TheSealStartedIt 16 points 2 years ago
This was a new one for me:
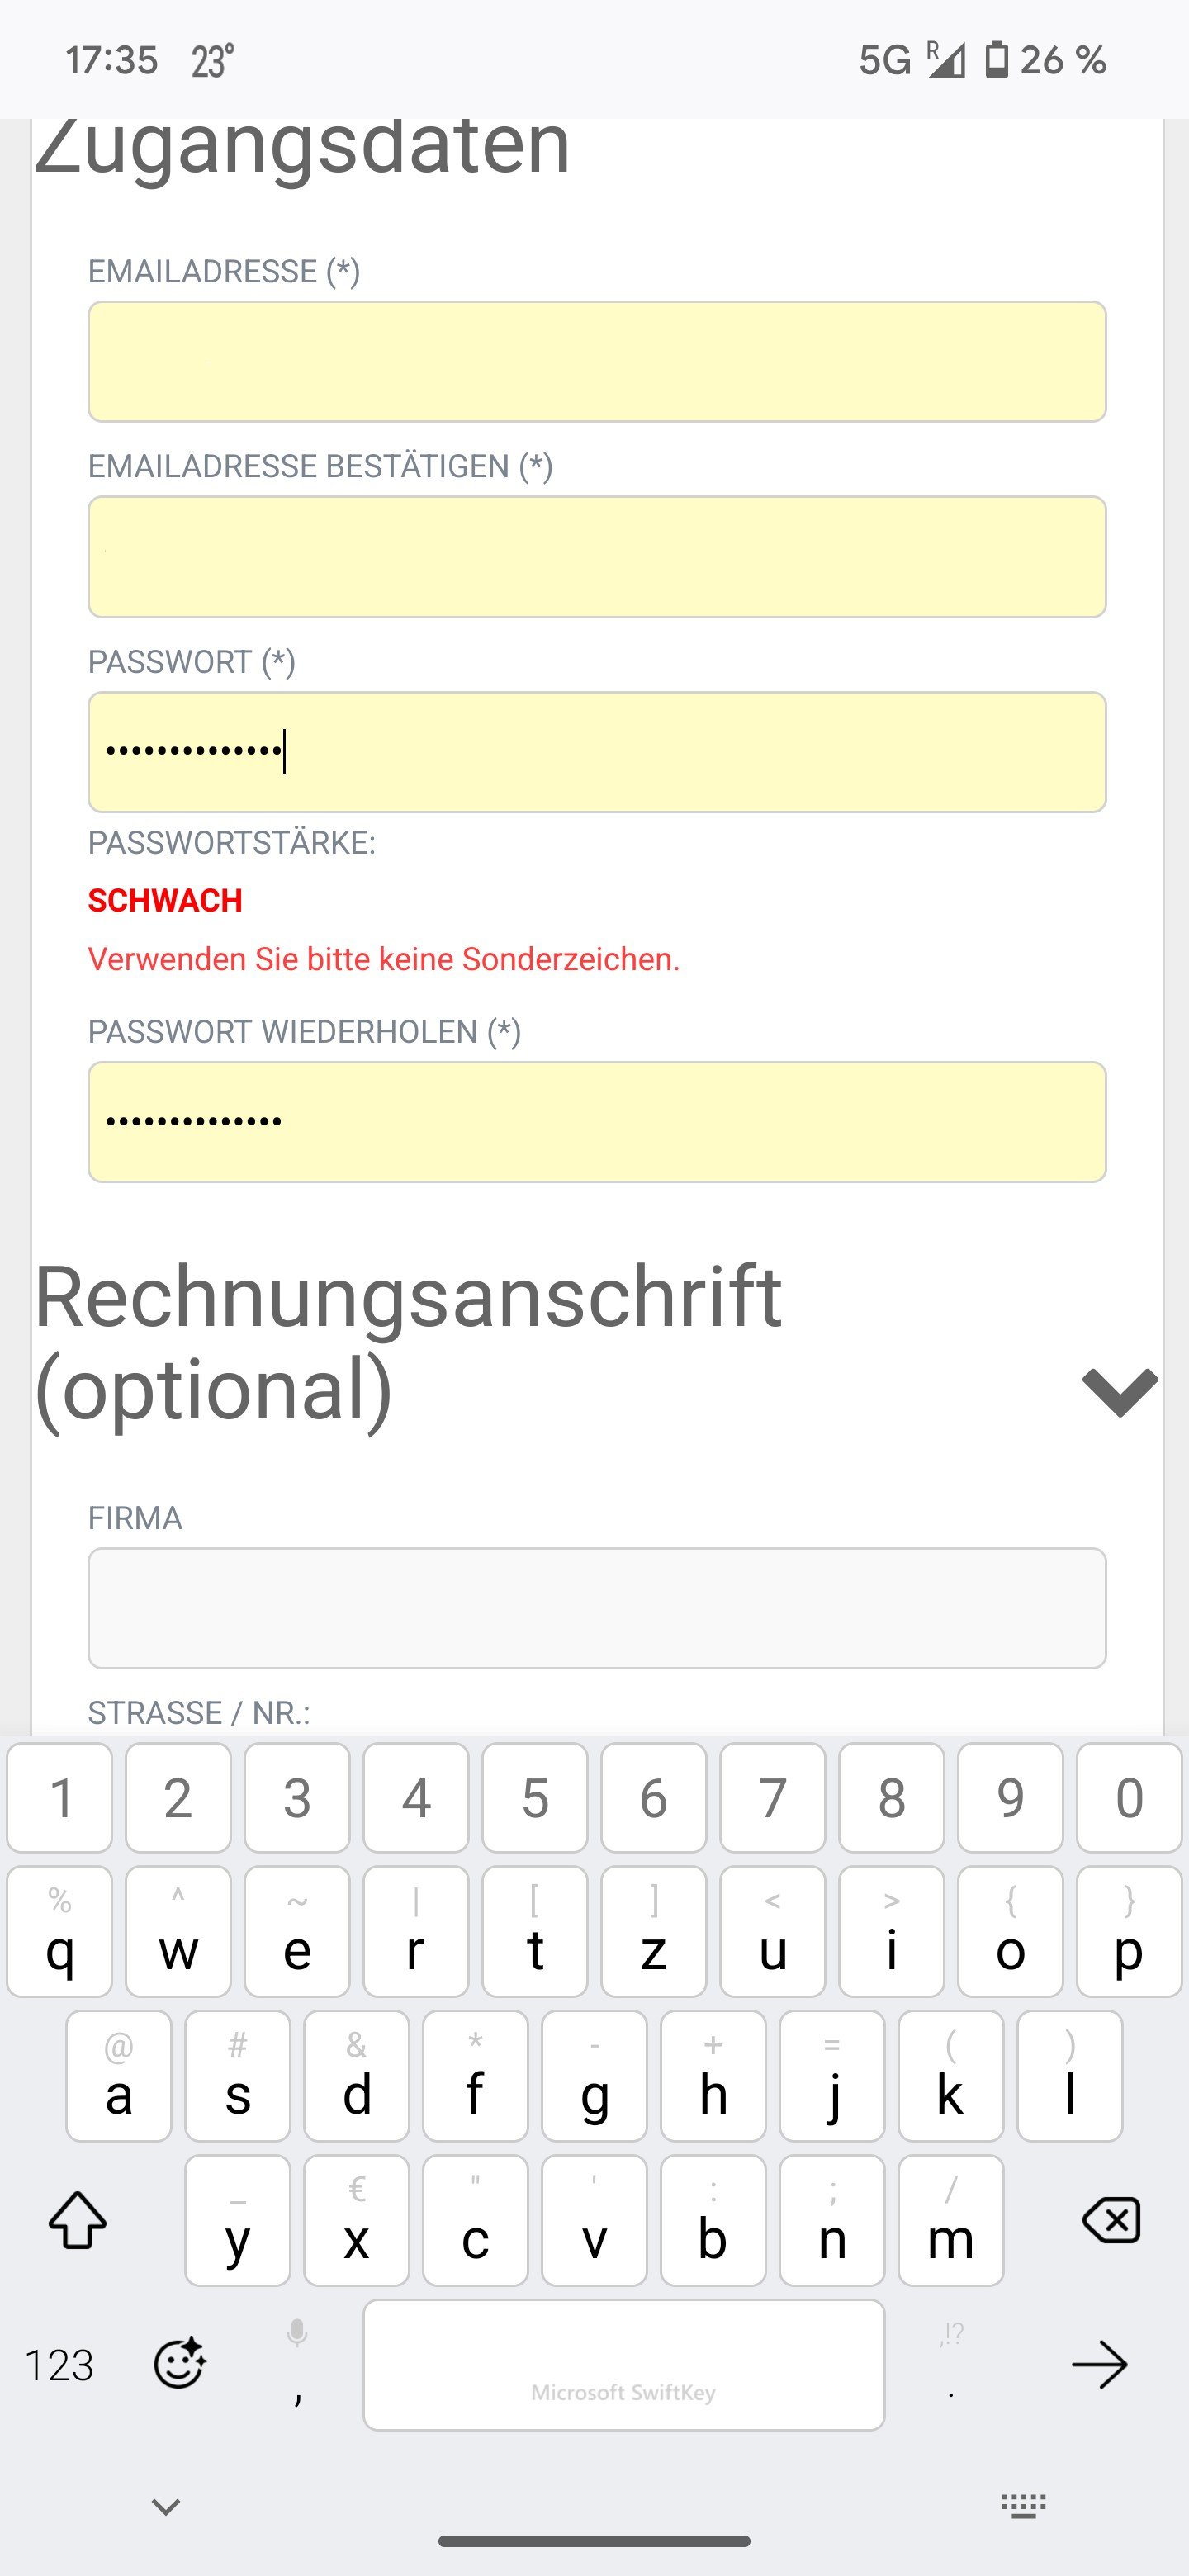
Translation: Password strength: weak. Please don't use any special characters.
It was a generated 14 char password.. (╯°□°)╯︵ ┻━┻)
FuglyDuck 12 points 2 years ago
My guess is they mean, one capital letter, one lower case letter, a number, and a special character
what's always amused me about these rules is that they exist because people are dumb. Technically, they lower the difficulty of the passwords slightly. ( for example, knowning that one character is a number reduces it to 10 options in stead of 10+26+26+whatever set of special characters)
anyhow. people should use password managers. just saying.
merc 12 points 2 years ago
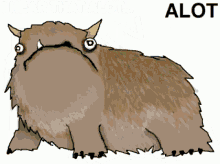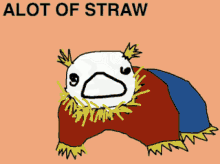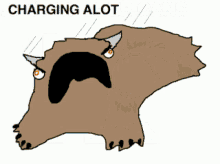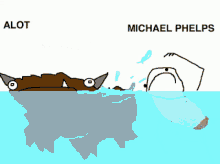
Noone should of aloud this code to go out the door. Atleast alot of other people people probably complained aswell, so your apart of a bigger group, incase you were worried.
spoiler
And yes, this was painful to type.
_stranger_ 18 points 2 years ago
Artyom 11 points 2 years ago
When commas and semicolons aren't allowed special characters
corsicanguppy 10 points 2 years ago
Please tell me someone didn't buy software with 'atleast' spelled like that in there. Please, tell me someone tested the web app and had the brains God gave a douglas fir and knew that wasn't a word; that it was never a word; that the writer's spell check should have picked that up; that it's not been over-ruled by stupid so much that it just takes it.
addie 8 points 2 years ago
Well now. When we've been enforcing password requirements at work, we've had to enforce a bizarre combination of "you must have a certain level of complexity", but also, "you must be slightly vague about what the requirements actually are, because otherwise it lets an attacker tune a dictionary attack against you". Which just strikes me as a way to piss off our users, but security team say it's a requirement, therefore, it's a requirement, no arguing.
"One" special character is crazy; I'd have guessed that was a catch-all for the other strange password requirements:
- can't have the same character more than twice in a row
- can't be one of the ten-thousand most popular passwords (which is mostly a big list of swears in russian)
- all whitespace must be condensed into a single character before checking against the other rules
We've had customers' own security teams asking us if we can enforce "no right click" / "no autocomplete" to stop their users in-house doing such things; I've been trying to push back on that as a security misfeature, but you can't question the cult thinking.
Wizard_Pope 5 points 2 years ago
Why do they think no copy paste is safer?
addie 8 points 2 years ago
Because if you disable browser autocomplete, what's obviously going to happen is that everyone will have a text file open with every single one of their passwords in so that they can copy-paste them in. So prevent that. But what happens if you prevent that is that everyone will choose terrible, weak passwords instead. Something like September2025! probably meets the 'complexity' requirement...
NigelFrobisher 3 points 2 years ago
“Atleast”?
cheers_queers 0 points 2 years ago
it's British. they also do "aswell"
NigelFrobisher 4 points 2 years ago
No we don’t.
Angry_Autist 3 points 2 years ago
You are using a special character that is likely reserved internally
bandwidthcrisis 2 points 2 years ago
The USCIS site makes it clear that your CAN use emojis in your password.
ETA: but not required.

programmer_humor
@programming.dev
33596
2558
7290
Welcome to Programmer Humor!
This is a place where you can post jokes, memes, humor, etc. related to programming!
For sharing awful code theres also Programming Horror.
Rules
- Keep content in english
- No advertisements
- Posts must be related to programming or programmer topics
- If the mod doesn't find it funny, you're banned. Ha-ha!... For real: do not use the community for "statements". There are other places for such content. Keep it chill and funny.
go to feed...
It's fucking insane that an internet banking portal has such a low cap on max characters and such shitty rule enforcement.
save